🚀 A CloudSEK se torna a primeira empresa de segurança cibernética de origem indiana a receber investimentos da
Leia mais


Pharming is a cyberattack that redirects users from a legitimate website to a fraudulent copy by tampering with the systems that translate web addresses into server locations. Victims type the correct address, see the correct address in the browser, and reach an attacker's server anyway.
Scale is what makes the technique worth an attacker's effort. Researchers tracking one DNS hijacking method counted roughly 800,000 domains still exposed to it and more than 70,000 already hijacked, with hundreds more falling every day.
Pharming fuses phishing and farming, and the second half of that name carries the meaning. A phishing email lures one recipient at a time, whereas a single poisoned DNS record harvests every visitor who requests that domain.
Attackers chase the same prize either way: banking credentials, card numbers, session tokens, and logins for corporate systems. Method is what separates them. Pharming corrupts the lookup process itself instead of persuading somebody to click a bad link.
Removing the click removes the human error most security training targets. No suspicious link exists to spot, because the victim navigates exactly as intended.
Pharming splits into two families: malware-based pharming, which rewrites settings on the victim's own device, and DNS-based pharming, which corrupts the lookup infrastructure everyone shares. Four vectors dominate, ordered here by how close each one sits to the victim.
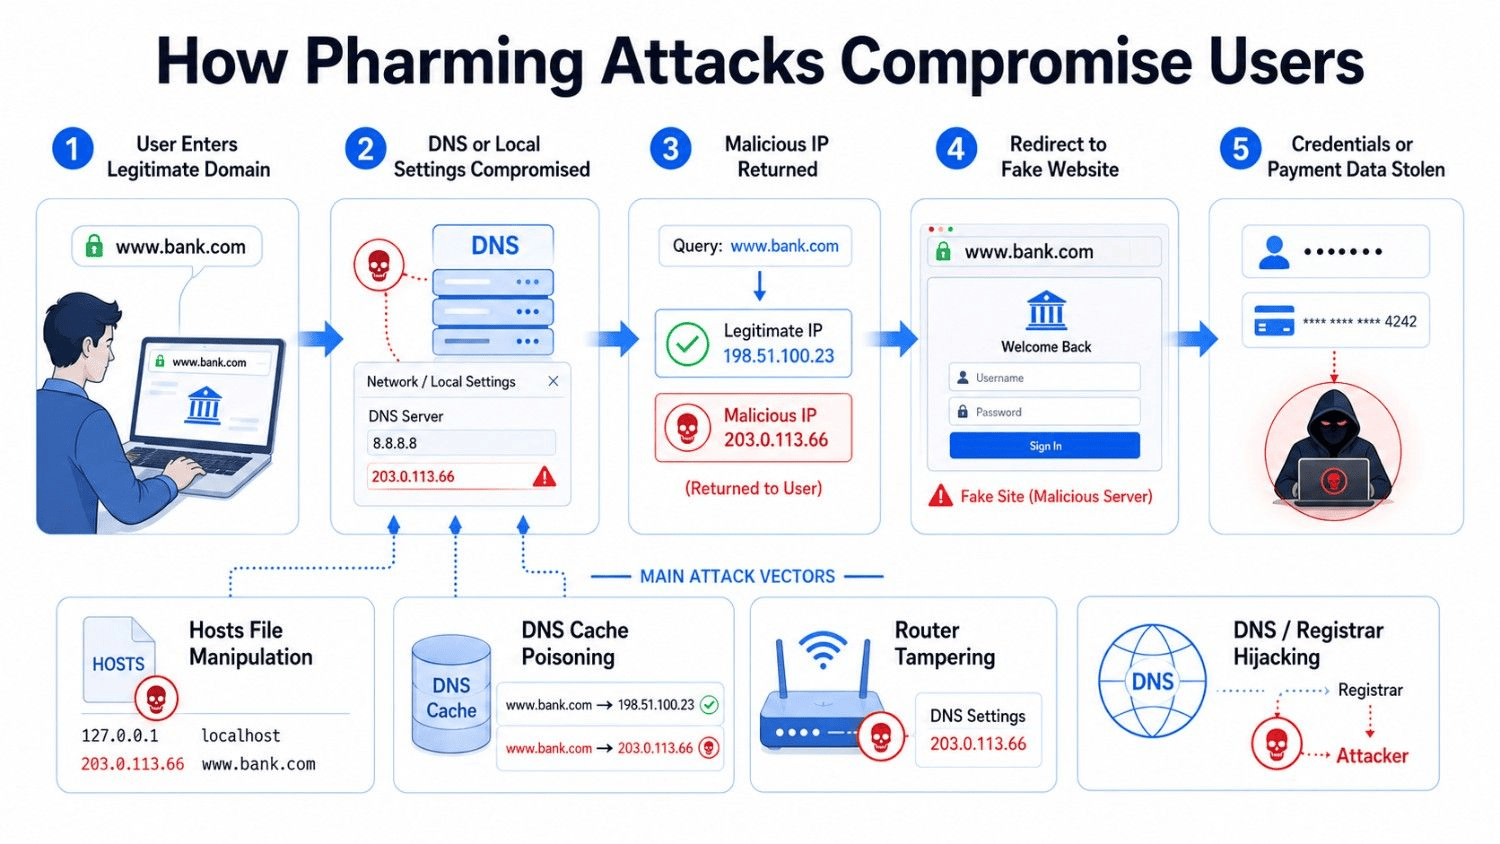
Every operating system keeps a local hosts file that maps domain names to addresses before any external lookup happens. Malware that edits this file pins a bank's domain to an attacker's server permanently, and the redirection survives reboots, network changes, and a switch of DNS provider.
Resolvers store answers temporarily to speed up repeat lookups. Cache poisoning injects a forged record into that store, so everyone using the resolver receives the attacker's address until the entry expires. Source-port randomization and DNSSEC have made this unreliable against modern resolvers, which pushed attackers toward the vectors below.
Consumer routers carry their own DNS settings, and many ship with default credentials that owners never change. An attacker who reaches the admin panel, often through a request forged by a malicious page, repoints the router at a rogue resolver and captures every device on that network.
Control of the domain itself produces the cleanest result. Attackers who compromise a registrar account, defeat weak ownership checks at a DNS provider, or claim an abandoned delegation decide where the domain resolves globally, with no malware on any victim device.
Both attacks end at a fake login page, and the route there differs entirely.
Standard phishing advice collapses against this technique. Checking the sender, hovering over links, and typing addresses manually all assume the danger sits in the link, when pharming corrupts the destination behind an address that is genuinely correct.
Certificate validation stays the one reliable tell. An attacker who controls DNS rarely holds a valid certificate for the domain, so the browser raises a warning, though users dismiss those warnings routinely.
Reputation scoring compounds the problem whenever a hijacked domain is involved. Security tools weigh a domain's history, and a hijacked domain arrives with years of clean standing, so filters that catch newly registered lookalikes let it through without comment.
Cache poisoning dominates most explanations of pharming, and it is the vector that has aged worst. Hardened resolvers made it unreliable, so the centre of gravity moved up to the domain layer.
Lame delegation opened that door. A domain delegates DNS duties to a provider; the provider never receives or later loses the records, and the delegation ends up pointing at name servers holding no authority for it.
Attackers exploit the gap by claiming the orphaned domain at the DNS provider, which hands them control of where it resolves without ever touching the registrar account. Researchers named the technique Sitting Ducks and track several criminal groups running it continuously, using the hijacked domains for phishing, fake investment schemes, and malware delivery.
Governments treat this layer as critical infrastructure. CISA issued its first emergency directive in January 2019 after a global DNS hijacking campaign reached multiple federal agency domains. Agencies received ten business days to audit every public DNS record and secure the accounts able to change them.
These campaigns show the range of the technique, from mass malware to router exploitation.
Banking campaign (2007). A coordinated attack hit customers of more than 50 financial institutions across the US, Europe, and Asia-Pacific, among them Barclays, PayPal, and American Express. Victims who reached a targeted bank were served a fake copy that captured their credentials before passing them along to the real site.
Operation Ghost Click (2011). DNSChanger malware infected roughly 4 million computers across more than 100 countries, rewriting DNS settings on machines and on some wireless routers. A two-year FBI investigation traced $14 million in fraudulent advertising revenue to an Estonian ring before dismantling it.
Brazilian router campaign (2015). Emails posing as a major telecom operator carried links that forged requests against UTStarcom and TP-Link routers, brute-forcing default admin credentials and repointing each router's DNS at a rogue server.
Damage scales with the layer an attacker controls, and it rarely stops at one stolen password:
Pharming hides well by design, though several indicators surface while it runs:
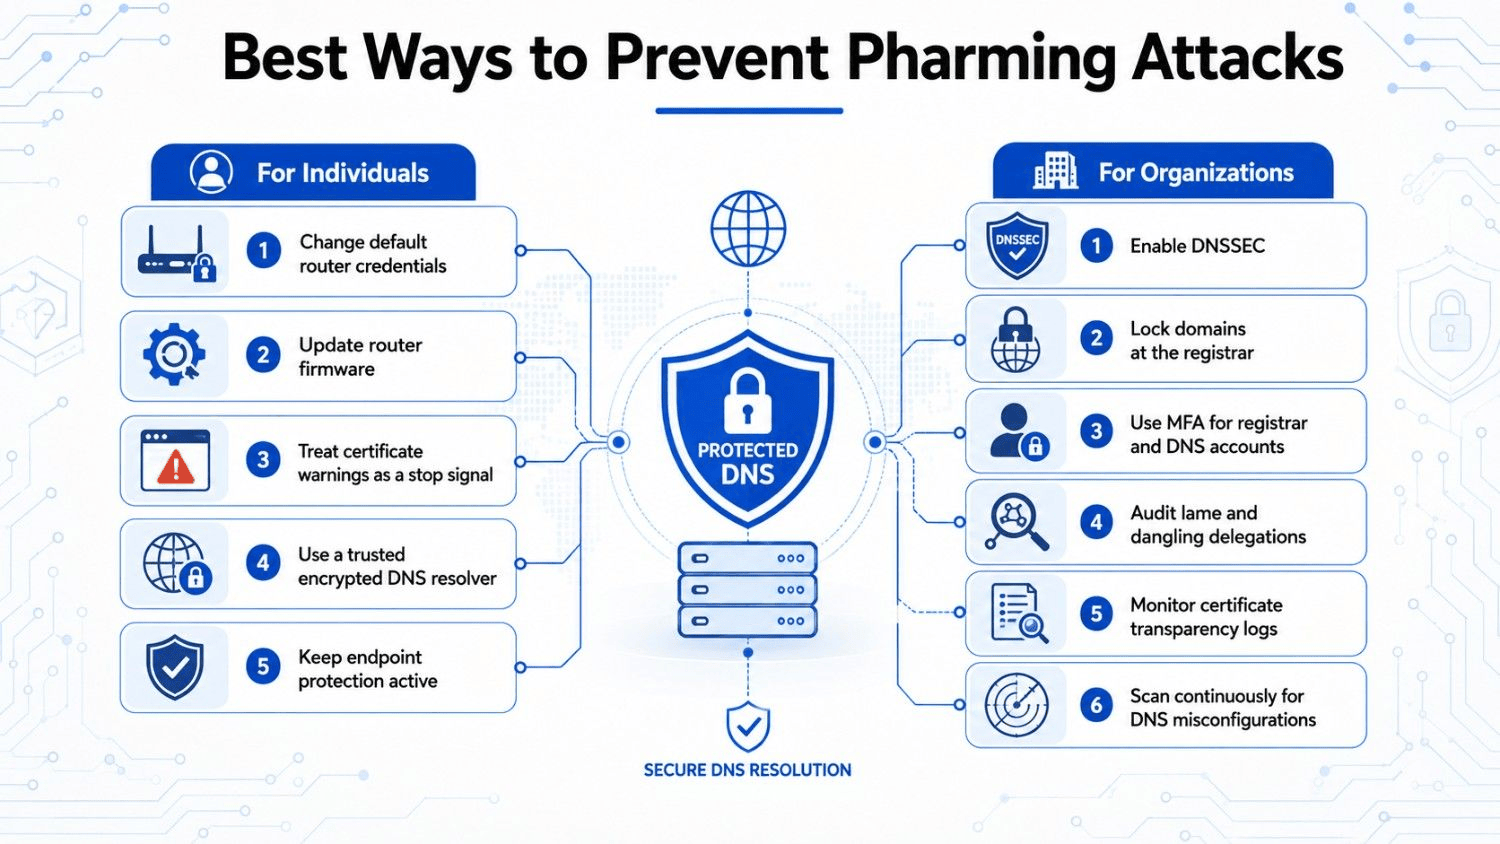
Defenses split by who controls the affected layer, because a home router and a corporate registrar account fail in different ways.
Every pharming campaign rests on infrastructure: a rogue resolver, a hijacked domain, or a cloned site staged for the redirect. Dismantling that infrastructure ends a campaign faster than waiting for victims to report it.
CloudSEK's XVigil runs a permutation engine that generates and tracks lookalike variations of a brand's domains, surfacing typosquatted and cloned sites across the surface, deep, and dark web, including domains advertised in underground forums before they go live.
Confirmed threats move into domain takedown, where CloudSEK recorded more than 2,200 takedowns in Q4 2024 at a 96 percent success rate, averaging about 4.1 business days. BeVigil covers the configuration side, flagging the DNS and certificate weaknesses that make hijacking possible in the first place.
Yes, pharming is illegal worldwide under computer-fraud, wire-fraud, and identity-theft statutes. Operating a rogue DNS server to redirect traffic carries criminal liability independent of any data actually stolen.
A VPN prevents pharming that depends on a compromised local network or router, because queries resolve through the provider instead. It offers no protection against a hijacked domain or an edited hosts file.
Drive-by pharming is an attack where visiting a malicious page alone triggers a script that changes the DNS settings on the visitor's router. Unchanged default router credentials make it work.
Pharming redirects traffic by corrupting DNS resolution, while spoofing covers any impersonation of a trusted identity, including emails, addresses, and websites. Pharming is one method of achieving website spoofing.
Yes, pharming can affect phones and tablets, since they resolve domains through the same DNS infrastructure. Joining a compromised Wi-Fi network exposes them exactly as it does laptops.
Isolate the affected resolver, router, or domain configuration to stop the redirection. Preserving DNS records and logs as evidence comes next, followed by credential resets once the redirect path is closed.
