🚀 A CloudSEK se torna a primeira empresa de segurança cibernética de origem indiana a receber investimentos da
Leia mais


Cerber ransomware is file-encrypting malware that pioneered the ransomware-as-a-service model in 2016, renting itself to affiliates who kept the larger share of every ransom they collected. One name now covers two distinct threats separated by eight years.
First came a 2016 Windows wave that Microsoft tracked across two delivery channels, malicious spam attachments and the RIG exploit kit, with later versions built to encrypt 493 distinct file types. Second came a 2024 Linux variant striking enterprise Confluence servers, a target unlike anything in the original consumer wave.
Cerber ransomware carries a consistent identity across its versions, encrypting files, appending a distinctive extension, and demanding Bitcoin through a ransom note that reads itself aloud.
Cerber ransomware works in three phases: it reaches a system through a delivery channel, encrypts files with a layered cipher, and hides its code from analysis. Each phase evolved across the malware's lifespan.
Phishing carried Cerber in its earliest campaigns. Malicious Word documents attached to spam email ran VBScript macros on the victim's confirmation, downloading the payload through a trojan loader that Microsoft tracked as Donoff.
Exploit kits opened a second, click-free path. RIG, Magnitude, and Neutrino kits scanned visitors to compromised websites for outdated Flash, Silverlight, and browser versions, then exploited flaws such as CVE-2015-8651 to install Cerber with no user action. Later intrusions used offensive frameworks including Cobalt Strike and Sliver.
Cerber uses a hybrid cipher, encrypting file contents with a symmetric algorithm and locking that key with asymmetric RSA so only the attacker's private key reverses it. Early builds paired RSA with the RC4 stream cipher, and later variants moved to AES-256 for file encryption, generating a unique key per infection.
Extension behavior shifted across versions. Initial releases appended .cerber, and subsequent builds switched to a random four-character extension unique to each victim, which complicated signature-based recovery.
Cerber payloads ship packed with UPX, which stores the real code encoded inside the binary and unpacks it into memory at runtime to defeat static scanning. Heavily obfuscated C++ resists reverse engineering across every payload.
Geographic and environment checks guard execution. Early Cerber terminated if it detected a system in several former Soviet states, and separate routines probed for the sandbox conditions that malware analysts rely on.
Cerber's business model drove its scale more than any technical feature. A developer advertised the malware on a criminal forum in February 2016 and recruited affiliates who kept 60% of each ransom while the developer took the remaining 40%.
Volume followed from that division of labor. Affiliates ran many concurrent distribution campaigns while the developer focused on the malware, shipping updates almost weekly to stay ahead of decryptors and detection tooling.
The affiliate model itself was the innovation. Recruitment, payment splitting, and campaign infrastructure all ran through darknet channels, and continuous dark web monitoring of those forums is how researchers first mapped Cerber's scale and later its decline.
Cerber moved through six major versions between 2016 and 2017, each adjusting extensions, delivery, or evasion. Version changes tracked the developer's response to decryption tools and detection.
After years of near-total dormancy, Cerber resurfaced in 2024 against Linux servers. Researchers at Cado Security, now part of Darktrace, documented a Cerber variant deployed onto Atlassian Confluence servers, a target profile with no resemblance to the 2016 consumer campaigns.
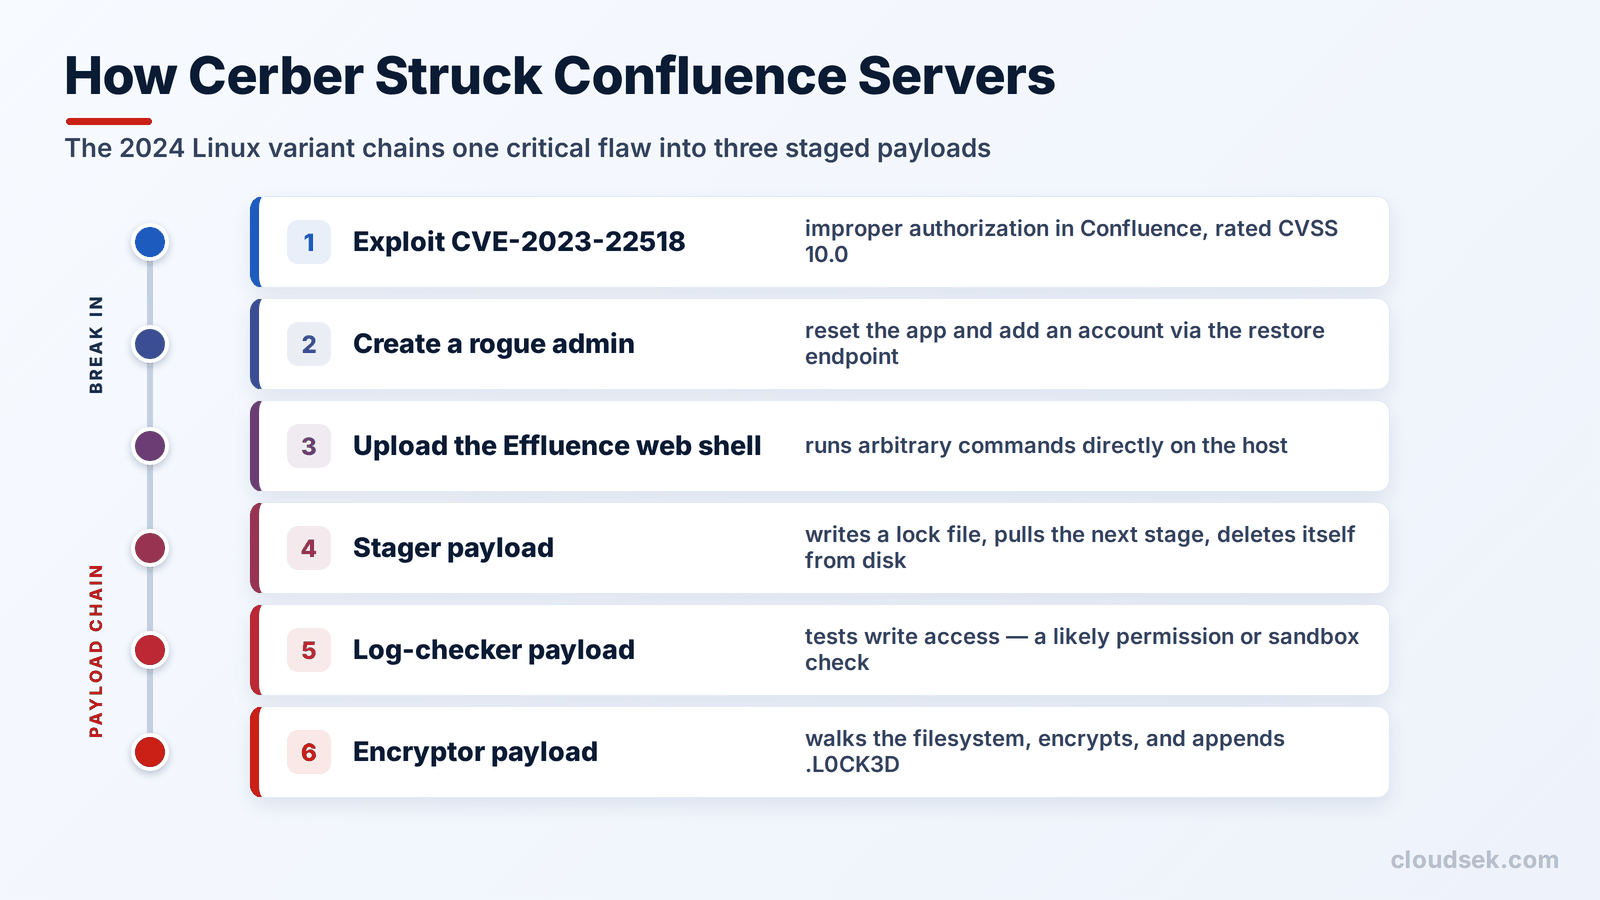
Access began with an improper-authorization vulnerability in Confluence Data Center and Server, tracked as CVE-2023-22518. Atlassian escalated the flaw to CVSS 10.0, the highest rating on the scale, after observing ransomware exploitation in the wild.
The vulnerability let an attacker reset the application and create a new administrator account through an unprotected configuration-restore endpoint. That account then uploaded the Effluence web shell, which runs arbitrary commands on the host.
Cerber's Linux variant runs as three UPX-packed C++ payloads. A primary stager writes a lock file, pulls a secondary payload from a command-and-control server, and deletes itself from disk while continuing in memory.
The second payload, a log checker, tests write access to a target directory, likely a permission or sandbox check. The third payload, the encryptor, walks the root filesystem, drops a ransom note in each writable directory, overwrites file contents with their encrypted form, and appends a .L0CK3D extension.
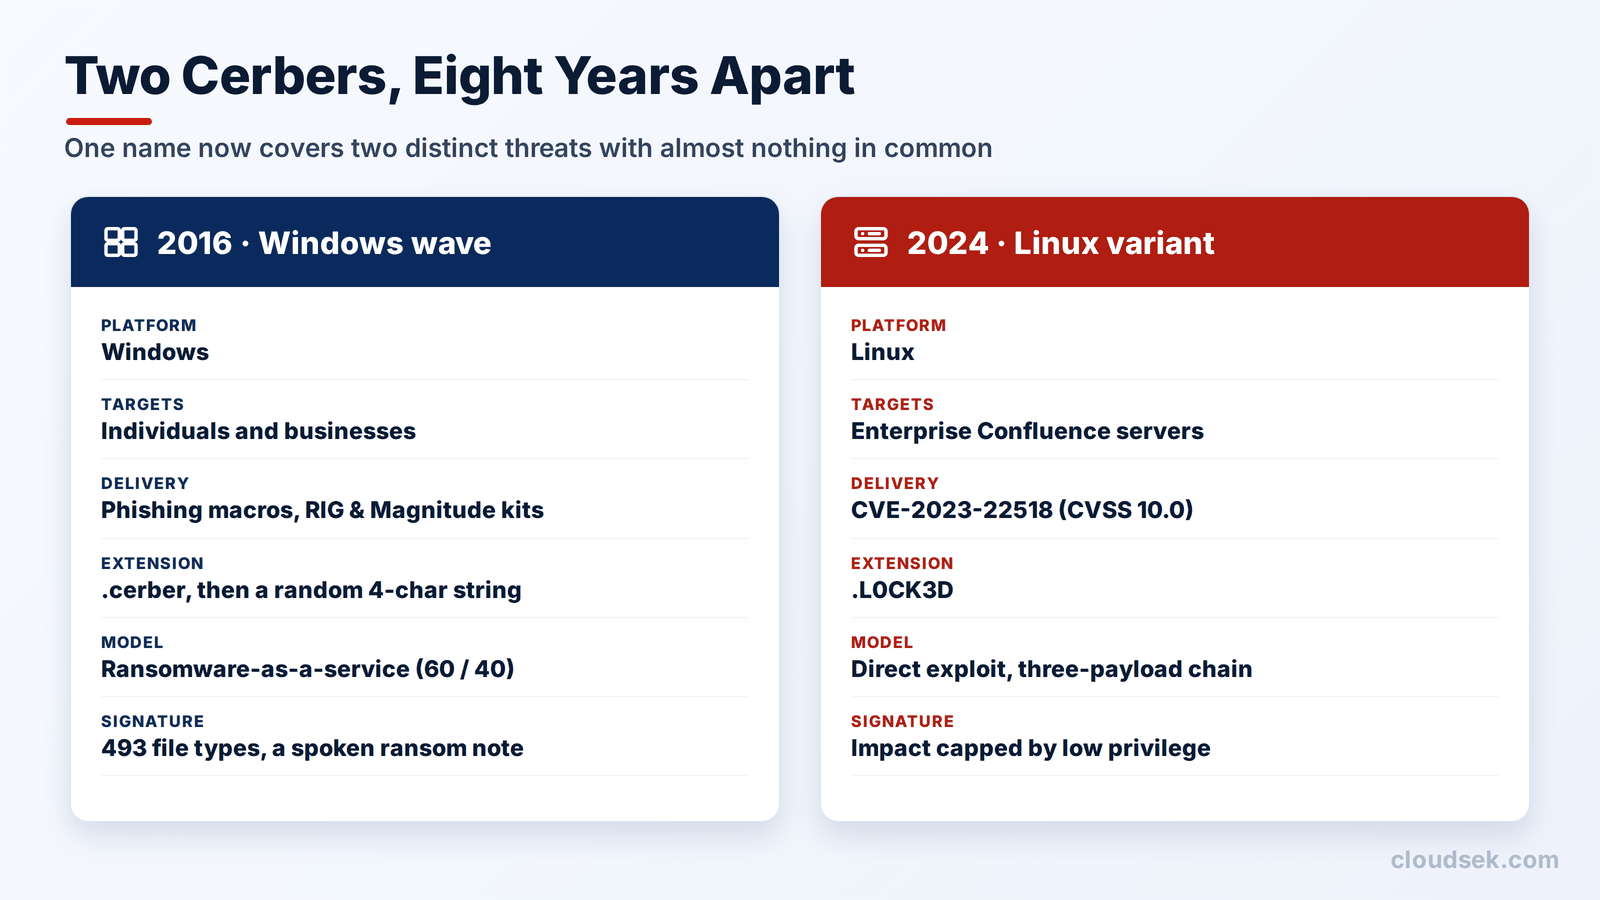
Privilege bounds the damage. Confluence typically runs as a low-privilege user, so the encryptor reaches only files that the user owns rather than the whole system. Well-configured servers keep backups of the Confluence datastore, which further reduces the leverage the encryption provides, and the ransom note's claim of data theft went unsupported by observed behavior.
Cerber's activity traces a clear arc across three phases.
Detecting Cerber ransomware combines file-system artifacts with behavioral signals, since packing defeats simple signature scanning.
Cerber's behavior maps to several MITRE ATT&CK techniques, which lets detection engineers align rules to each stage of an infection.
To remove Cerber ransomware and recover files, work through six steps, and set expectations honestly on the limits of decryption.
Preventing Cerber and similar ransomware means closing the entry paths every version relied on. Broader ransomware prevention guidance extends these controls, and documented ransomware attack examples show the same gaps recurring across families.
Is Cerber ransomware still active?
Cerber ransomware is still mostly inactive in its original form, having declined to near zero by 2018, though a Linux variant revived the Cerber name against Confluence servers in 2024.
Can Cerber-encrypted files be decrypted?
No, most Cerber-encrypted files cannot be decrypted. Free tools cracked early 2016 versions, but later builds use secure encryption with no known decryptor, leaving backups as the recovery path.
What file extension does Cerber ransomware add?
Cerber ransomware adds the .cerber file extension in early versions, a random four-character extension in later Windows builds, and a .L0CK3D extension in the 2024 Linux variant.
Does Cerber ransomware steal data or only encrypt it?
Cerber ransomware primarily encrypts data rather than stealing it. Its 2024 Linux ransom note claimed exfiltration, but researchers observed no data-theft behavior supporting that claim.
What made Cerber ransomware different from other ransomware?
What made Cerber ransomware different was its early ransomware-as-a-service model and its audio ransom note, which read the demand aloud and earned it the name the ransomware that speaks.
Does Cerber ransomware affect Linux?
Yes, Cerber ransomware does affect Linux through a 2024 variant. This Cerber ransomware variant affects Linux Confluence servers via CVE-2023-22518, encrypting files owned by the low-privilege Confluence user.
