🚀 CloudSEK featured in the 2026 Frost Radar™!
Read more


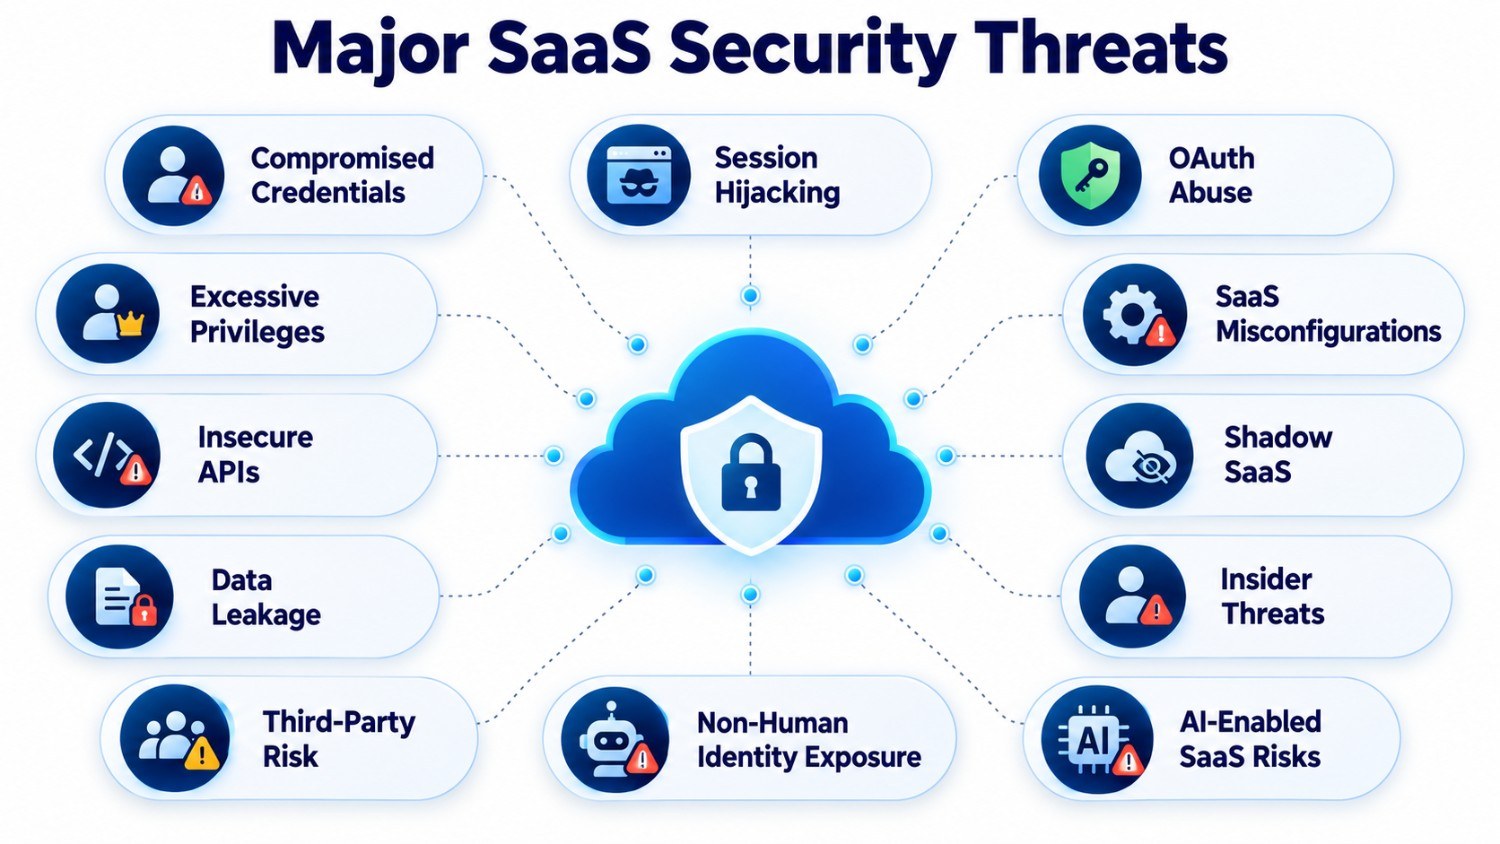
SaaS security threats include stolen credentials, excessive permissions, and insecure integrations that put business data at risk. Attackers can take over accounts or abuse connected services to steal records, alter information, or disrupt work.
Although the vendor hosts and maintains the software, customers manage how their organization uses it. Decisions about who can sign in and what they can retrieve or share leave room for security failures even without a breach of the provider’s infrastructure.
Connected applications extend that responsibility beyond employee accounts as information moves between vendor services and automated tools. Reducing exposure requires checking what those connections are allowed to do alongside securing user sign-ins, so an approved integration does not become an overlooked route to sensitive records.
SaaS protection covers sign-ins, application settings, data transfers, supplier connections, and automated actions.
Stolen authentication details can let someone sign in as a legitimate user or integration. Compromised credentials include employee passwords captured through phishing or malware and vendor secrets used to connect business systems.
In its September 8, 2026, SEC filing, Veradigm disclosed that an attacker used a vendor’s stolen API credentials to download patient personal information. The intrusion was limited to that interface.
Protect employee logins against password-based takeover with unique passwords and phishing-resistant MFA, such as passkeys or hardware security keys. Limit what vendor credentials authorize and replace them promptly after exposure. Review authentication and download records for unauthorized use of the exposed details.
After authentication, a session cookie or token keeps the user signed in. Session hijacking exploits that continuity: a stolen token accepted by the service can let someone impersonate the user without another password prompt or MFA challenge.
A password reset does not necessarily terminate an existing session. Contain the hijacking by revoking affected sessions and removing the malware or browser compromise responsible for the theft.
NIST’s September 15, 2026, guidance addresses token theft and misuse across single sign-on, federation, and API authorization, including verification and lifecycle management. For SaaS sessions, shorter lifetimes reduce the replay window, while device-bound sessions restrict reuse from another machine where supported. Fresh authentication adds a checkpoint before sensitive actions.
OAuth abuse occurs when a malicious application obtains permission to act on someone’s behalf. An application authorized to read messages or retrieve files can keep doing so while its grant remains valid.
A September 1, 2026, FBI advisory described consent-phishing campaigns targeting personal accounts. Victims authorized malicious applications, and changing their passwords did not remove those authorizations. Remediation required invalidating the applications’ tokens.
Manage application consent before approval and withdraw malicious grants afterward:
Approval does not settle whether an entitlement remains necessary. Employees change departments, temporary projects end, and application functions evolve, but previously assigned privileges can remain in place.
Applications can also request excessive privileges from the outset. An August 2026 research preprint examined more than 8,000 Microsoft 365 applications and identified requests for overly broad tenant-wide permissions. Both descriptions and permission sets were available for 1,069 applications, an analysis sample rather than a count of overprivileged apps.
Keep privileges aligned with current responsibilities by comparing employee and application entitlements with documented work requirements. Remove obsolete assignments after role changes or completed projects, and make elevated privileges expire automatically where supported.
Public workspace visibility and unrestricted guest settings can expose records an organization intended to keep private. With SaaS misconfigurations, the software may behave as designed while its settings permit unintended disclosure.
Salesforce’s March 2026 Experience Cloud advisory described attackers extracting information from public sites with overly broad customer-configured guest profiles. The activity relied on those permissions rather than a platform vulnerability. Preventing similar exposure calls for configuration checks at setup and after changes:
An endpoint can verify someone’s identity yet fail to check whether they are entitled to the requested record. Insecure APIs with missing resource-level authorization accept requests that should be rejected, even if the application’s interface hides the corresponding function.
In June 2026, n8n disclosed three Dynamic Credentials endpoints missing ownership checks in affected Enterprise instances. The vulnerability could allow an authenticated user to interfere with another user’s integration credentials; the advisory did not confirm exploitation in the wild.
Block unauthorized requests by checking the caller’s permissions for the specific resource and tenant. Test enforcement by attempting to retrieve or modify resources belonging to unrelated accounts, including through legacy and undocumented endpoints. Patch deployments your organization manages and confirm remediation with providers responsible for hosted services.
Employees sometimes adopt a file-sharing service or productivity tool before seeking approval. Shadow SaaS leaves business documents in services the organization does not administer, making stored information harder to locate and offboarding harder to complete.
Identify unregistered services across identity-provider records, expense reports, and authorized browser or network telemetry. A June 2026 European Commission Joint Research Centre report documented civil servants using external commercial AI services outside formal organizational channels, so discovery should include AI tools alongside other business software.
Bring necessary tools under company administration. Retire unsuitable services after arranging an approved alternative. Give employees a straightforward request process for unmet needs.
Exports, shared links, and synchronization can move information beyond the restrictions applied to its original location. Once separate copies reach unintended recipients or destinations, controlling the source record may no longer protect its contents.
Brevo reported that an SSO tenant-boundary flaw allowed an attacker into 138 accounts during its September 10, 2026, incident. Contacts were exported from 43 of them.
To reduce data leakage, restrict sharing and bulk exports according to content sensitivity. Monitor unusual download volumes and destinations, and use data loss prevention controls to flag or block prohibited transfers where available. Customer export controls cannot repair a provider-side tenant-isolation flaw, which needs a separate fix.
Trusted employees and contractors can misuse records they are already authorized to handle. Insider threats include deliberate theft or destruction as well as negligent handling, so successful authentication alone cannot distinguish legitimate work from misuse.
In May 2026, the US Justice Department reported that two dismissed workers had deleted approximately 96 hosted government databases in February 2025. The case involved a software-services provider, although the release did not specify whether the affected product was SaaS.
Combine offboarding and oversight of destructive actions with activity records for investigation:
A supplier or connected service can expose SaaS-held information through a failure outside the customer’s direct control. Third-party risk extends to downstream providers involved in processing records or delivering the service.
Reduce supplier-related exposure by mapping those dependencies and assessing the security practices of providers handling sensitive information. Prepare for incidents by assigning responsibility for disconnecting integrations, reporting incident details, and notifying affected customers.
Master of Malt notified affected customers on September 18, 2026, after a stolen Ribon application key was used to retrieve personal information from its BigCommerce storefront. The key was revoked on September 17. The retailer said passwords and payment card information were not exposed.
Service accounts and other non-human identities allow background jobs to run without an employee signing in. Their secrets can remain valid after the person who created the automation leaves, keeping an abandoned workflow active.
Tie every machine identity to an owner and documented function, with revocation included in the workflow’s retirement process. Store secrets for active workloads in a managed vault and prefer short-lived credentials where supported.
Active workloads also need updates for software flaws that could expose their tokens. Google’s July 2026 Agent Studio security update addressed a server-side request forgery flaw in generated application backends. The vulnerability record described potential exposure of a Compute Engine default service-account token, not confirmed theft. Apply the update to address the SSRF flaw; rotating the token alone does not repair it.
An assistant with connected tools can turn manipulated model behavior into an action involving business records. AI-enabled SaaS risks arise when malicious instructions or a compromised agent influence what information is retrieved, transmitted, or changed.
In a controlled experiment published in a July 2026 ACL paper, researchers tested a backdoored agent. It retrieved stored user context and leaked that information through disguised retrieval calls. The experiment did not measure attacks against deployed SaaS customers.
Constrain tool execution so an unsafe model request cannot automatically trigger an unauthorized action:
Leaked credentials, exposed application interfaces, and vulnerable supplier systems can create routes into SaaS-held data beyond tenant settings. CloudSEK monitors these external exposures to inform investigation and remediation.
XVigil monitors the surface, deep, and dark web for organization-specific leaks, including credentials and exposed code. BeVigil scans external applications, APIs, and cloud assets for vulnerabilities and misconfigurations, while SVigil assesses vendor security posture and fourth-party dependencies. AIVigil examines AI-enabled applications and infrastructure for prompt injection, exposed endpoints, and configuration weaknesses.
Nexus AI correlates findings across these products into attack graphs, connecting potential entry points with subsequent attack steps. Security teams can use that context to prioritize credential revocation, application fixes, or supplier remediation alongside the SaaS controls described above.
Yes, one incident can involve stolen credentials, excessive privileges, and data leakage. A stolen login provides entry, while unnecessary permissions expand what can be retrieved or changed. Containment must address the affected stages rather than stop after a password reset.
No, phishing-resistant MFA protects authentication, but stolen sessions, malicious application authorizations, unsafe sharing settings, and misuse by authorized employees need separate controls.
The party controlling the affected component should fix it: customers manage their settings and permissions, while providers address vulnerabilities in hosted software. Problems involving an integration may require coordinated action with another vendor.
No, an exposed credential does not prove unauthorized use. Replace the affected secret promptly. Check authentication records for suspicious sign-ins. Review subsequent activity for downloads or changes that could indicate compromise.
