🚀 Introducing the CloudSEK MCP Server!
Read more


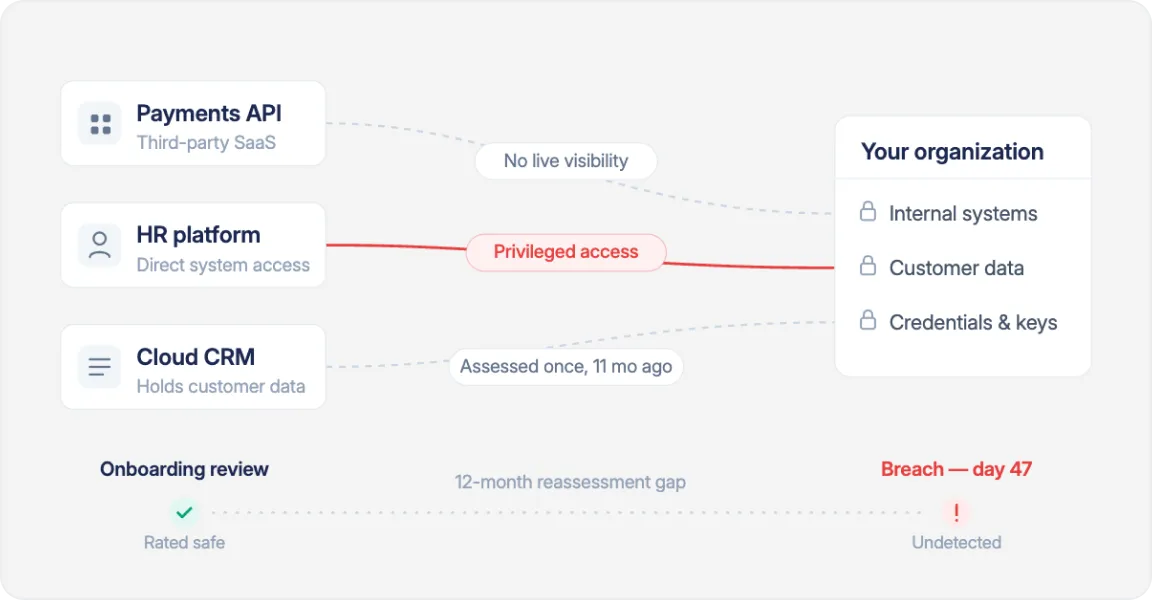
SVigil is CloudSEK's AI-native third-party and supply chain attack surface intelligence platform. It monitors vendors continuously and maps hidden dependencies to pinpoint vendor-driven initial access vectors before attackers exploit them.


Global Enterprises and Fortune 500 companies trust CloudSEK to fortify their cybersecurity posture.
Ongoing vendor monitoring vs. point-in-time checks
Hidden dependencies mapped across the supply chain
Vendors & suppliers monitored continuously
Integrations across your security ecosystem
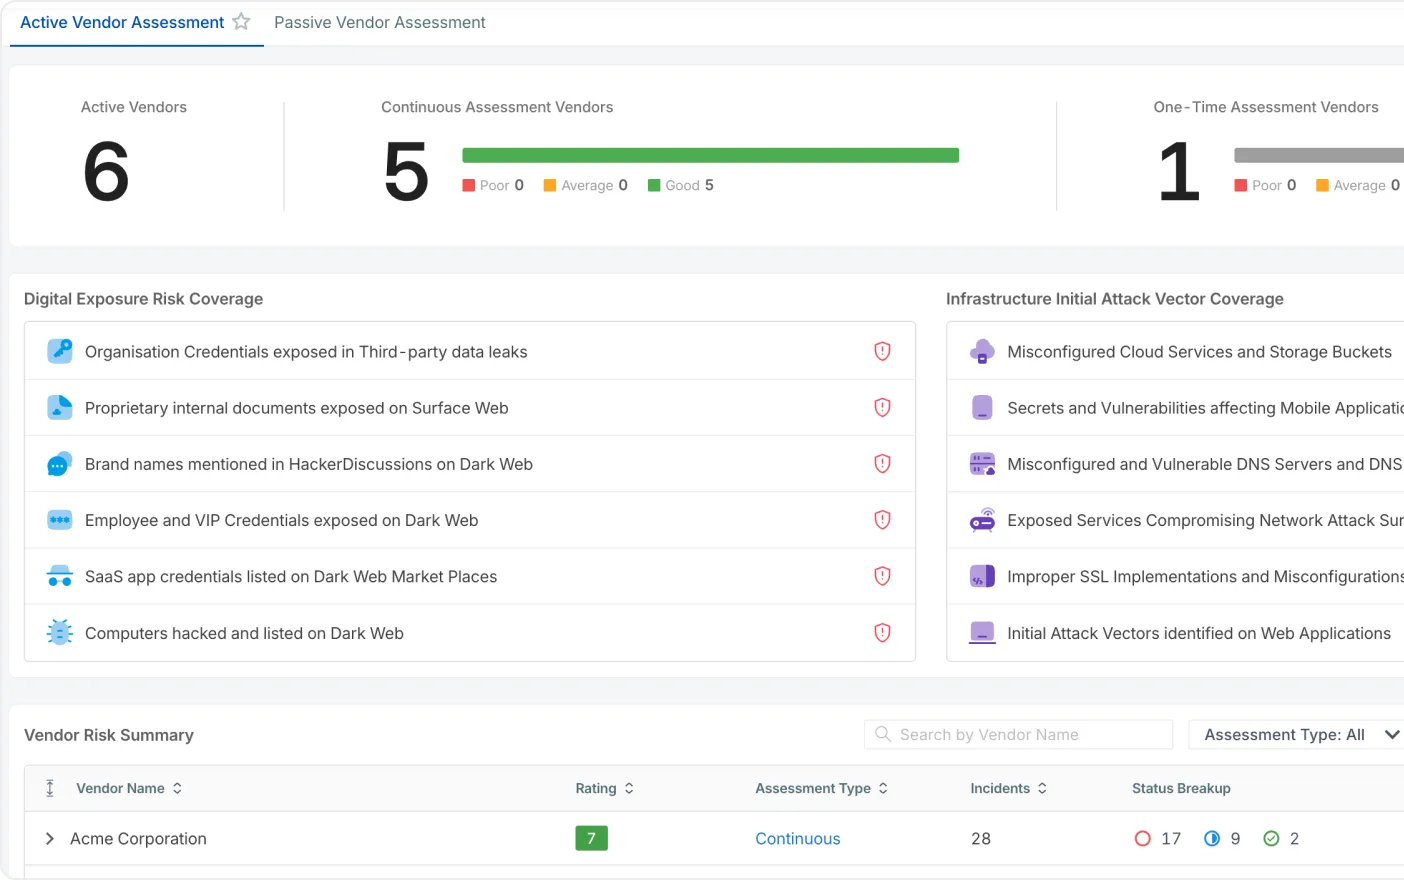
SVigil continuously monitors vendor exposures, identifies exploitable risks, and uses Nexus AI to prioritize the attack paths that could impact your organization.
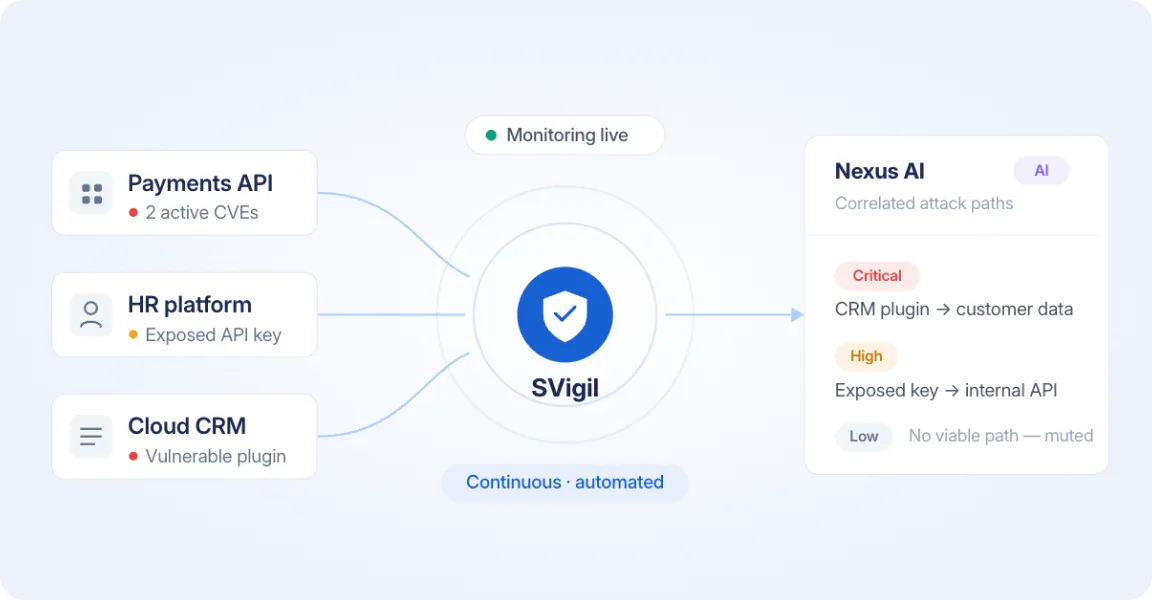
Real-time discovery of changing vendor security postures.

Uncovers software components and hidden sub-vendor entry points.
Pushes findings into your existing stack (SIEM, SOAR, TIP).
Not every leak or mention is a threat. XVigil filters the noise and surfaces what's actually worth acting on.

Critical web/mobile app vulnerabilities & bad SSL setups

Misconfigured API endpoints & critical cloud asset risks

DNS server misconfigurations & exposed network services

Known CVEs in software and services

Vendor email leaks & dark web compromised logs

Proprietary code, secrets, & documents on public/API platforms

Dark web market listings, hacker forum chatter, & chat apps
CloudSEK SVigil assesses the risks and vulnerabilities introduced by third-party suppliers and vendors that may impact the security of an organization's products or services.

Real-time ratings and historical tracking to prioritize critical gaps.

Discovers vendor domains, IPs, web/mobile apps, and cloud assets.

Choose on-demand snapshot scans or continuous vendor tracking.

Direct vendor invite system with actionable guidance to fix gaps.

Maps vendor asset distribution to pinpoint regional infrastructure risk.

Prioritizes exposures attackers can actually chain into an attack path.

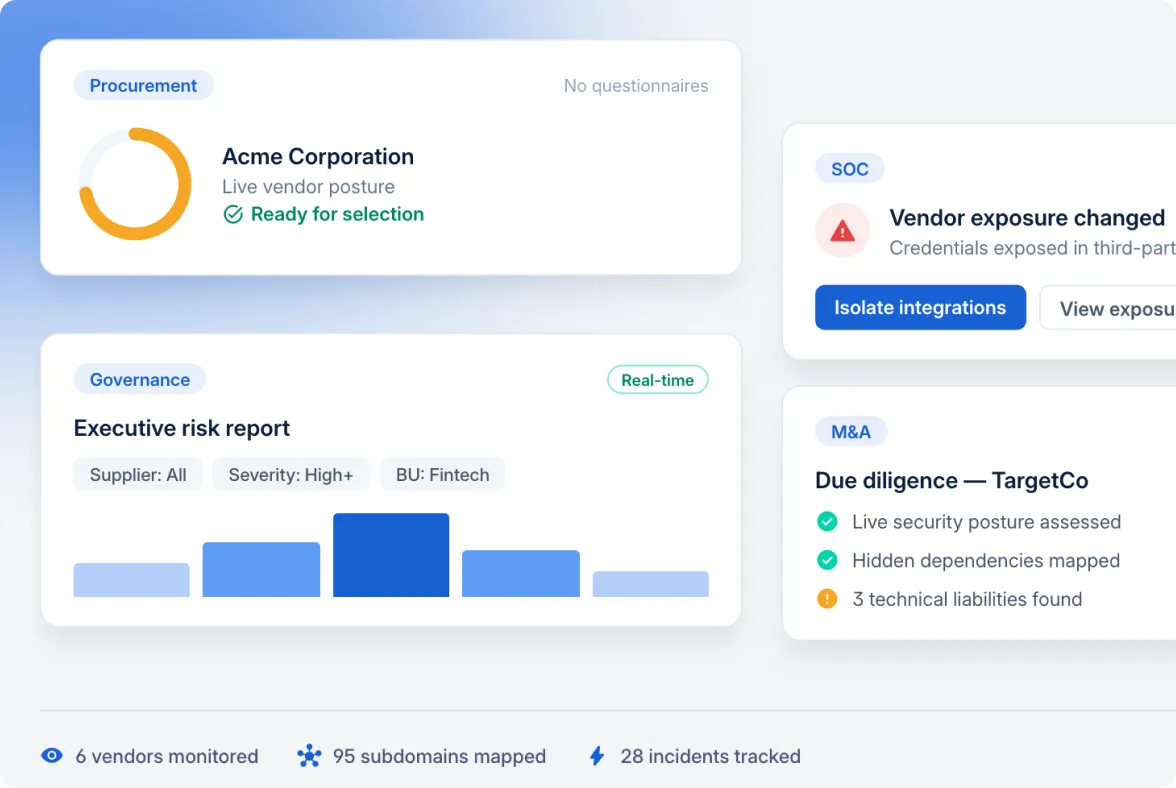
Replaces slow questionnaire chasing with live observed posture.
The exposure that matters shifts by sector. XVigil tunes detection to what each one is targeted for.

Safeguard core banking integrations, APIs, and partner software networks.

Protect patient data and connected clinical platforms from third-party vendor breaches.

Secure payment gateway integrations, supply chain logistics systems, and SaaS plugins.

Continuously audit open-source dependencies and software vendor supply chains.
The difference between watching the dark web and knowing where you are exposed.


Integrate CloudSEK’s IAV intelligence via APIs and automate threat resolution across 50+ applications in your security ecosystem.
Integrate CloudSEK’s IAV intelligence via APIs and automate threat resolution across 50+ applications in your security ecosystem.
These answers keep SVigil grounded in the external attack surface category covering internet-facing assets, misconfigurations, vulnerabilities, and continuous monitoring.
SVigil is CloudSEK's continuous third-party and supply chain attack surface intelligence platform. It gives enterprises continuous visibility into the cyber posture of their vendors, partners, and supply chain dependencies, identifying vendor-driven initial access vectors and the hidden dependencies attackers use to reach an organization through its suppliers.

Vendor risk scoring platforms produce a score at a point in time. SVigil monitors vendors continuously, so risk is caught as it emerges rather than at the next assessment cycle. It also adds attacker context: findings are tied to real initial access vectors and correlated by Nexus AI into potential attack paths, rather than reported as a single number.
Fourth-party risk is the risk introduced by your vendors' own vendors and dependencies. Most programs assess direct suppliers and stop there. SVigil maps the hidden dependencies across the supply chain, so an organization can see the software, services, and providers its vendors rely on and where a compromise several steps away could still reach it.
Continuously. SVigil monitors vendors on an ongoing basis, not just at onboarding or during periodic review cycles. It turns vendor risk assessment from a periodic snapshot into a continuous operational intelligence program, so a change in a vendor's posture is visible when it happens.
SVigil monitors the elements of an organization's supply chain that carry risk, including vendor software, plugins, dependencies, third-party libraries, and the services and providers vendors rely on. It tracks vendor posture, exposure introduced through third-party data leaks, and the software supply chain components that can become entry points.
SVigil helps security and procurement teams assess, monitor, and act on third-party risk without manual evidence collection. Instead of chasing questionnaires and attestations, both teams work from the same continuously updated view of vendor posture, which supports onboarding decisions and ongoing oversight.
A vendor-driven initial access vector is an entry point into your organization that exists because of a supplier relationship, such as an exposed vendor system, a compromised software dependency, or credentials leaked through a third-party breach. SVigil identifies these vectors so they can be closed before an attacker chains them into an attack path.
Yes. SVigil integrates with existing SIEM, SOAR, TIP, and ticketing tools so third-party findings reach the workflows teams already run. Custom dashboards and reports can be built to show vendor risk by supplier, severity, and business unit.
SVigil prioritizes third-party risks by potential impact and severity, using contextual analysis and data fusion to connect related findings. Vendor findings feed Nexus AI, which correlates them into potential attack paths, so teams act on the vendor exposures that could actually be reached rather than a flat list of issues.
SVigil is the third-party and supply chain layer of CloudSEK's AI-native predictive cyber intelligence platform. The vendor-driven initial access vectors it identifies feed Nexus AI, which correlates them with findings from across the platform into potential attack paths. SVigil answers whether attackers can reach you through your vendors.
Stay updated with the Latest resources.
Walk through BeVigil coverage across web, mobile, API, cloud, DNS, SSL, CVE, and network surfaces.