🚀 أصبحت CloudSek أول شركة للأمن السيبراني من أصل هندي تتلقى استثمارات منها
اقرأ المزيد

Yahoo’s 2013 data breach stands among the biggest cyber attacks in history because the company later determined that approximately 3 billion accounts were affected. The scale of compromised information, however, cannot explain the historical significance of attacks such as Stuxnet or WannaCry. Stuxnet manipulated industrial control processes, whereas WannaCry disrupted NHS services in England, demonstrating how cyberattacks can cause damage that goes far beyond stolen data.
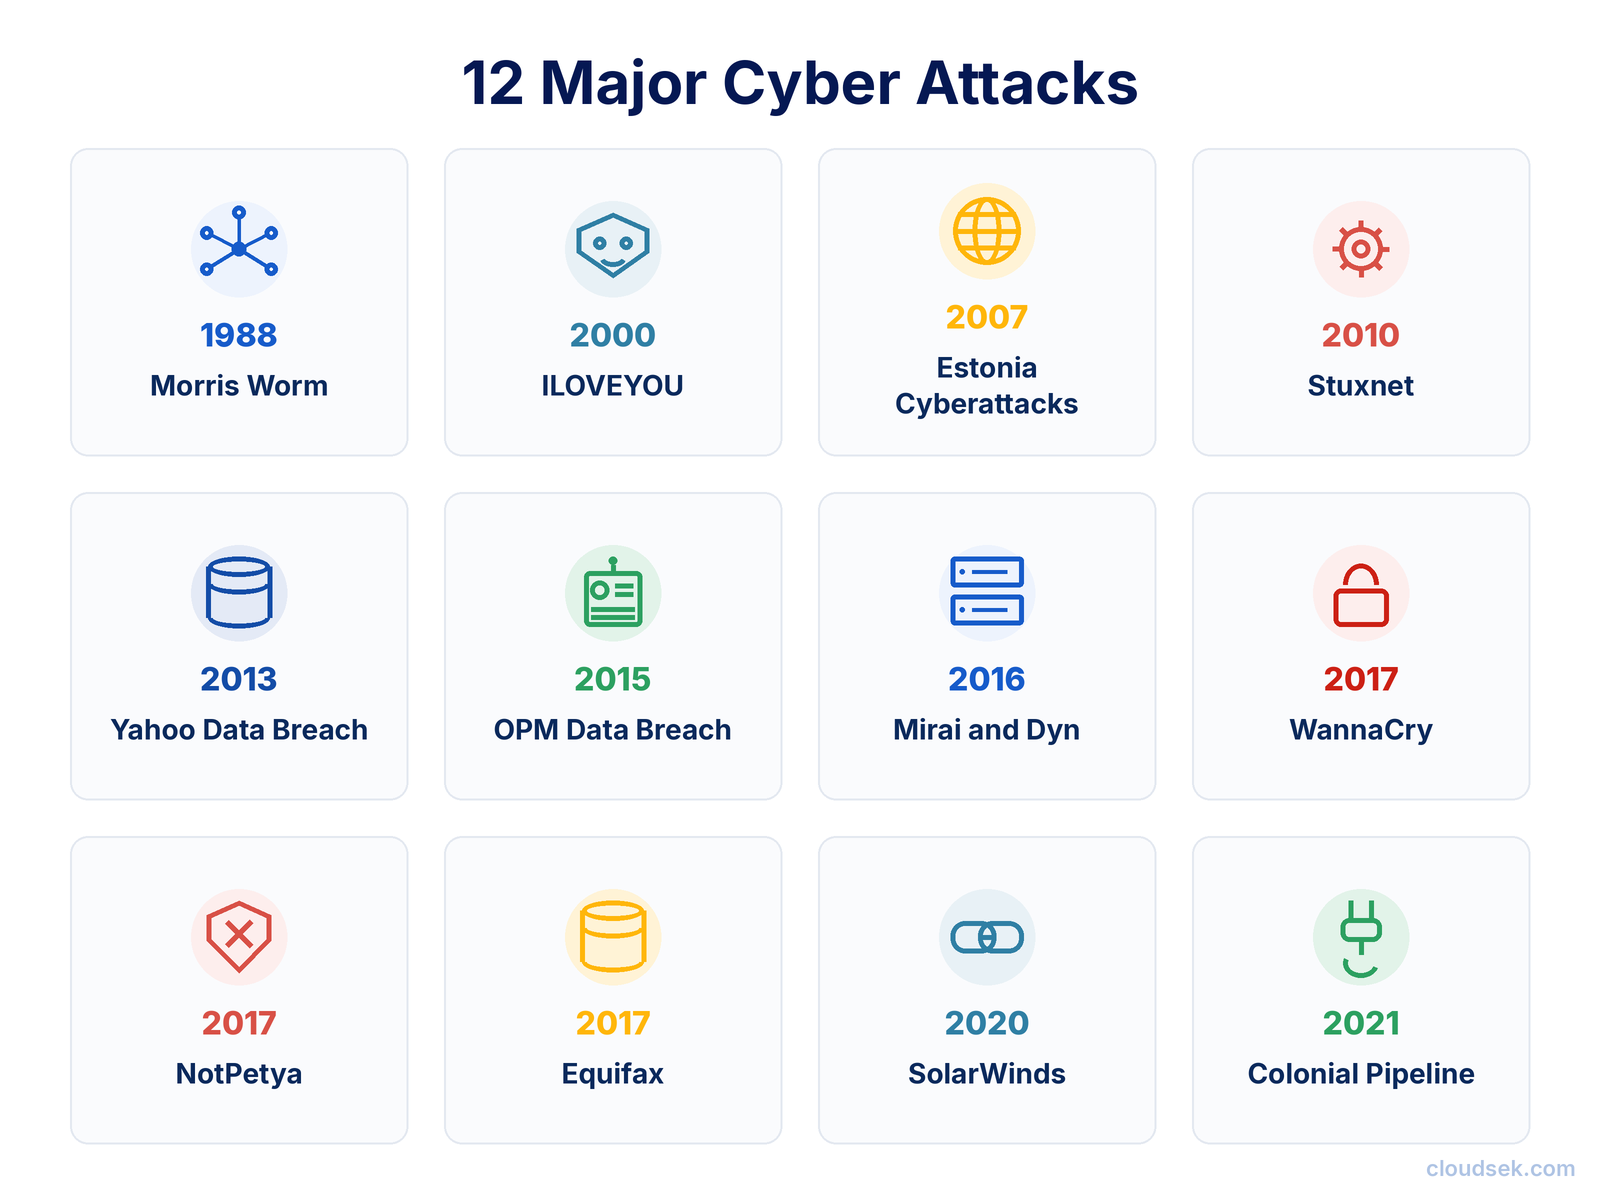
NotPetya and SolarWinds both exploited trusted software updates, but their consequences differed. NotPetya damaged disk structures and disrupted businesses, whereas SolarWinds enabled targeted espionage. The twelve incidents spanning 1988 to 2021 were selected for their documented reach, operational disruption, economic consequences, national security implications, and lasting influence on cybersecurity. They are grouped by year rather than ranked from most to least severe.
The Morris Worm spread through computers on the early internet in 1988, while the Colonial Pipeline ransomware incident brought fuel transportation to a halt in 2021. Between those events, major attacks compromised government records, disrupted DNS services, manipulated industrial controllers, and exploited trusted software updates.
Robert Tappan Morris released a computer worm on November 2, 1988, that spread between Unix machines connected to the early internet. The program exploited weaknesses in network services and attempted password guesses to reach additional hosts. Its reinfection logic allowed multiple copies to run on computers already carrying the worm. As these processes accumulated, they exhausted computing resources and left machines slow or unresponsive.
Approximately 6,000 of the estimated 60,000 internet-connected computers were affected within 24 hours, according to the FBI's historical account. Universities and research institutions faced widespread disruption as administrators attempted to restore their computing environments. The outbreak contributed to the creation of the CERT Coordination Center, while Morris later became the first person convicted under the Computer Fraud and Abuse Act.
An email titled “ILOVEYOU” began circulating internationally in May 2000 with an attachment named LOVE-LETTER-FOR-YOU.TXT.VBS. Its filename disguised an executable Visual Basic script as a personal letter, encouraging recipients to open it. Executing the attachment infected the computer and initiated further distribution without requiring the sender to compose another message.
Cyberattacks struck Estonia during April and May 2007 amid protests over the relocation of the Bronze Soldier memorial in Tallinn. The decision intensified political tensions involving Russia, and important online services became targets during the unrest. Government portals, banks, news organizations, and internet service providers faced coordinated waves of hostile traffic.
Distributed denial-of-service (DDoS) attacks overwhelmed websites and network connections, preventing legitimate requests from being processed. Customers struggled to reach online banking services, while public agencies and media outlets experienced interruptions to their digital communications. The primary consequence was loss of availability rather than demonstrated theft of sensitive records from the targeted institutions.
A NATO-affiliated study of the campaign examined the attribution challenges and their implications for national cyber defense. The incident influenced subsequent security measures in Estonia and wider international cooperation, but its political context alone did not prove state direction of individual attacks.
Stuxnet, discovered in 2010, contained code designed to recognize specific industrial environments running Siemens Step 7 and WinCC software. Windows computers served as a route toward programmable logic controllers (PLCs), which execute instructions governing industrial machinery. Infection alone was insufficient to activate the specialized sabotage routines because the equipment configuration had to match the intended target.
To reach those industrial environments, Stuxnet used several propagation methods, including removable media and exploitation of Windows vulnerabilities. Once it encountered compatible controllers, the payload altered instructions governing physical processes. Concealment routines interfered with the feedback available to operators, hiding unauthorized changes from ordinary monitoring.
Ralph Langner's To Kill a Centrifuge examined Stuxnet's targeting of uranium enrichment infrastructure at Iran's Natanz facility. The Symantec W32.Stuxnet Dossier separately documented its controller manipulation and concealment mechanisms. Together, these investigations established the malware's technical design, although they did not independently identify its sponsors or determine a definitive number of damaged centrifuges.
Yahoo suffered a major account-data theft in August 2013, but the incident remained undisclosed publicly until December 2016. The company said the stolen records may have included names, email addresses, telephone numbers, birth dates, hashed passwords, and security questions and answers. Its investigation did not indicate that plaintext passwords, payment card numbers, or bank account details had been taken.
Yahoo initially estimated that more than one billion accounts were involved. Further forensic work changed that assessment, and an October 3, 2017 SEC-filed announcement stated that the company believed all approximately 3 billion accounts existing in 2013 were affected. That figure represented account records rather than three billion verified individual victims.
The US Office of Personnel Management (OPM) disclosed two major intrusions in 2015 involving federal personnel files and background investigation databases. The breaches concerned separate but related collections of records maintained for government employment and security clearance purposes.
Dyn's managed Domain Name System (DNS) infrastructure experienced two major DDoS attacks on October 21, 2016. Mirai-based botnets contributed substantial traffic from compromised internet-connected devices, overwhelming infrastructure responsible for resolving domain names. Because numerous unrelated websites depended on Dyn, visitors encountered connection failures even when the underlying application servers had not been directly attacked.
Failed DNS queries prompted recursive resolvers to retry requests, compounding the hostile traffic and complicating estimates of botnet participation. In its original incident analysis, preserved by the Internet Archive, Dyn estimated up to 100,000 malicious endpoints while noting that traffic from millions of observed IP addresses included legitimate retry attempts.
When WannaCry spread internationally on May 12, 2017, Microsoft had already released a security update addressing the Windows Server Message Block (SMB) vulnerabilities the malware exploited. Unpatched computers remained susceptible, allowing worm-like propagation between reachable machines. On infected hosts, ransomware encrypted files and prevented employees from using applications and documents needed for daily work.
England's National Health Service experienced substantial disruption as hospitals struggled with unavailable computer systems. The UK National Audit Office reported that at least 81 of 236 NHS trusts were affected, including organizations disrupted without being directly infected. Hospitals canceled appointments, and several emergency departments diverted patients when essential clinical services became unavailable. The National Audit Office reported NHS Digital's assessment that patient data had not been compromised or stolen during the incident.
The outbreak occurred after NHS Digital had warned organizations about the exploited vulnerability in March and April 2017, yet vulnerable machines remained in service despite available security updates. The Department of Health also lacked a formal mechanism for checking whether local trusts had implemented the recommended protections.
Computers began failing across organizations in Ukraine on June 27, 2017, before the outbreak reached multinational businesses elsewhere. Infected machines displayed ransom demands, initially making the incident resemble conventional ransomware.
Attackers breached Equifax in 2017 through an internet-facing consumer dispute application running a vulnerable version of Apache Struts. A security patch had been available before the intrusion, but the company failed to identify and update the affected application. Exploitation of the flaw provided a route into connected databases holding sensitive consumer records.
According to the Federal Trade Commission's July 2019 announcement, approximately 147 million people were affected. Stolen data included names, Social Security numbers, dates of birth, and additional identifying details. The permanence of Social Security numbers made the breach particularly consequential because replacing a password does not invalidate an identifier used across financial and government processes.
A US Government Accountability Office investigation identified shortcomings in vulnerability identification, intrusion detection, database segmentation, and data governance. Monitoring deficiencies delayed recognition of suspicious behavior, while inadequate separation between applications and databases contributed to the attackers' ability to retrieve sensitive records.
The SolarWinds Orion compromise became public in December 2020, several months after customers received altered software updates. Attackers had inserted the SUNBURST backdoor into the vendor's software build process, allowing malicious code to enter releases distributed between March and June 2020. Installing those versions created an opportunity for further intrusion through a trusted software channel.
SolarWinds initially reported that up to 18,000 customers could have downloaded affected software. Following additional investigation, the company estimated in an SEC filing that fewer than 100 customers had been hacked through SUNBURST. Its assessment drew partly on sampled DNS communication data and distinguished potentially exposed downloads from downstream compromise.
An employee discovered a ransom note on Colonial Pipeline's corporate IT network on May 7, 2021. Subsequent investigation identified a legacy virtual private network (VPN) profile as the suspected intrusion route. CEO Joseph Blount told Congress that the company believed attackers exploited that profile, although the source of the credentials remained unknown. Mandiant, which led the investigation, said the account lacked multi-factor authentication and that its password was later found in a batch of leaked credentials on the dark web, possibly reused from another breached account, though investigators could not confirm that was how the attackers obtained it.
Concern about possible movement from business systems into operational technology prompted employees to halt pipeline transportation as a precaution. The decision stopped an approximately 5,500-mile network transporting fuel across the eastern United States. In his original congressional testimony, Blount described an effort to contain the intrusion rather than a response to proven attacker control of industrial equipment.
Fuel deliveries remained interrupted for several days, contributing to shortages in parts of the Southeast. Colonial subsequently resumed pipeline service while restoration of its corporate IT environment continued.
An available security patch did not guarantee protection, and a trusted update channel did not guarantee safe code. Beyond the initial breach, permissions, network reach, and dependencies between essential services influenced how far the consequences extended.
An internet-facing application is not automatically the most serious weakness in an organization. Its significance changes if stolen credentials or a supplier relationship create a route to sensitive systems. Evaluating that possibility requires connecting separate pieces of external evidence.
Several of the attacks above began with exposure that was visible from outside before it was exploited. Equifax ran an internet-facing application with a known, patchable Apache Struts flaw. Colonial Pipeline’s entry point was a legacy VPN account whose password later surfaced in a dark-web leak. NotPetya and SolarWinds reached their victims through trusted suppliers.
CloudSEK maps to each of these patterns. BeVigil identifies internet-facing assets and known vulnerabilities like the one behind Equifax, and CloudSEK Threat Intelligence flags which flaws attackers are actively exploiting. XVigil monitors dark-web markets and stealer logs for leaked credentials and validates whether they still work. SVigil continuously monitors suppliers for the weaknesses that turn a vendor into an entry point. Nexus AI correlates these findings into potential attack paths toward critical assets, so teams can fix the links that matter most first. A modeled chain represents a plausible route, not proof that an attacker has followed it.
