🚀 Introducing Cloudsek Launchpad: a incubator for early-stage cybersecurity founders, apply today!
Read more

Machine learning in cybersecurity is the use of algorithms that learn patterns from data to detect threats, flag anomalies, and automate defense without a hand-written rule for every attack. Machine learning is a subset of artificial intelligence, and it drives most modern threat detection, from malware classification to behavioral analysis.
Security teams turn to machine learning because attack volume outpaces manual analysis. Organizations that used AI and automation extensively across security operations saved an average of $1.9 million per breach and contained incidents 80 days faster, according to IBM's 2025 Cost of a Data Breach Report.
Machine learning works in cybersecurity by training models on security data, then using those models to predict whether new activity is malicious. Four stages define the process.
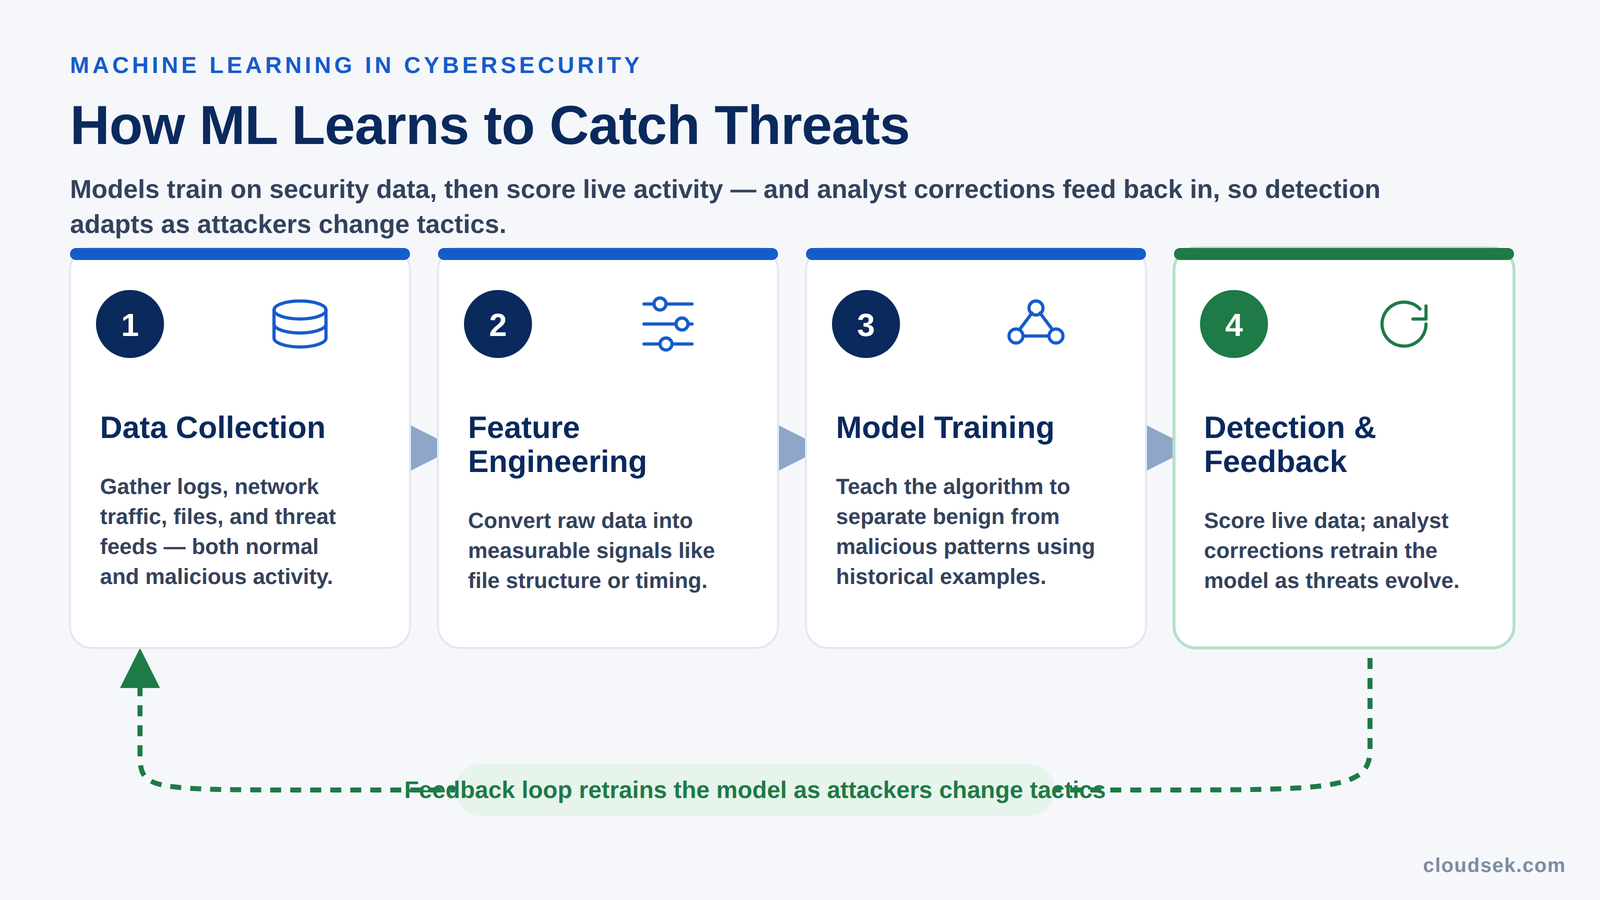
This feedback loop lets models adapt as attackers change tactics, which signature-based tools alone cannot match.
Cybersecurity uses three core learning approaches and deep learning - each suited to different detection tasks.
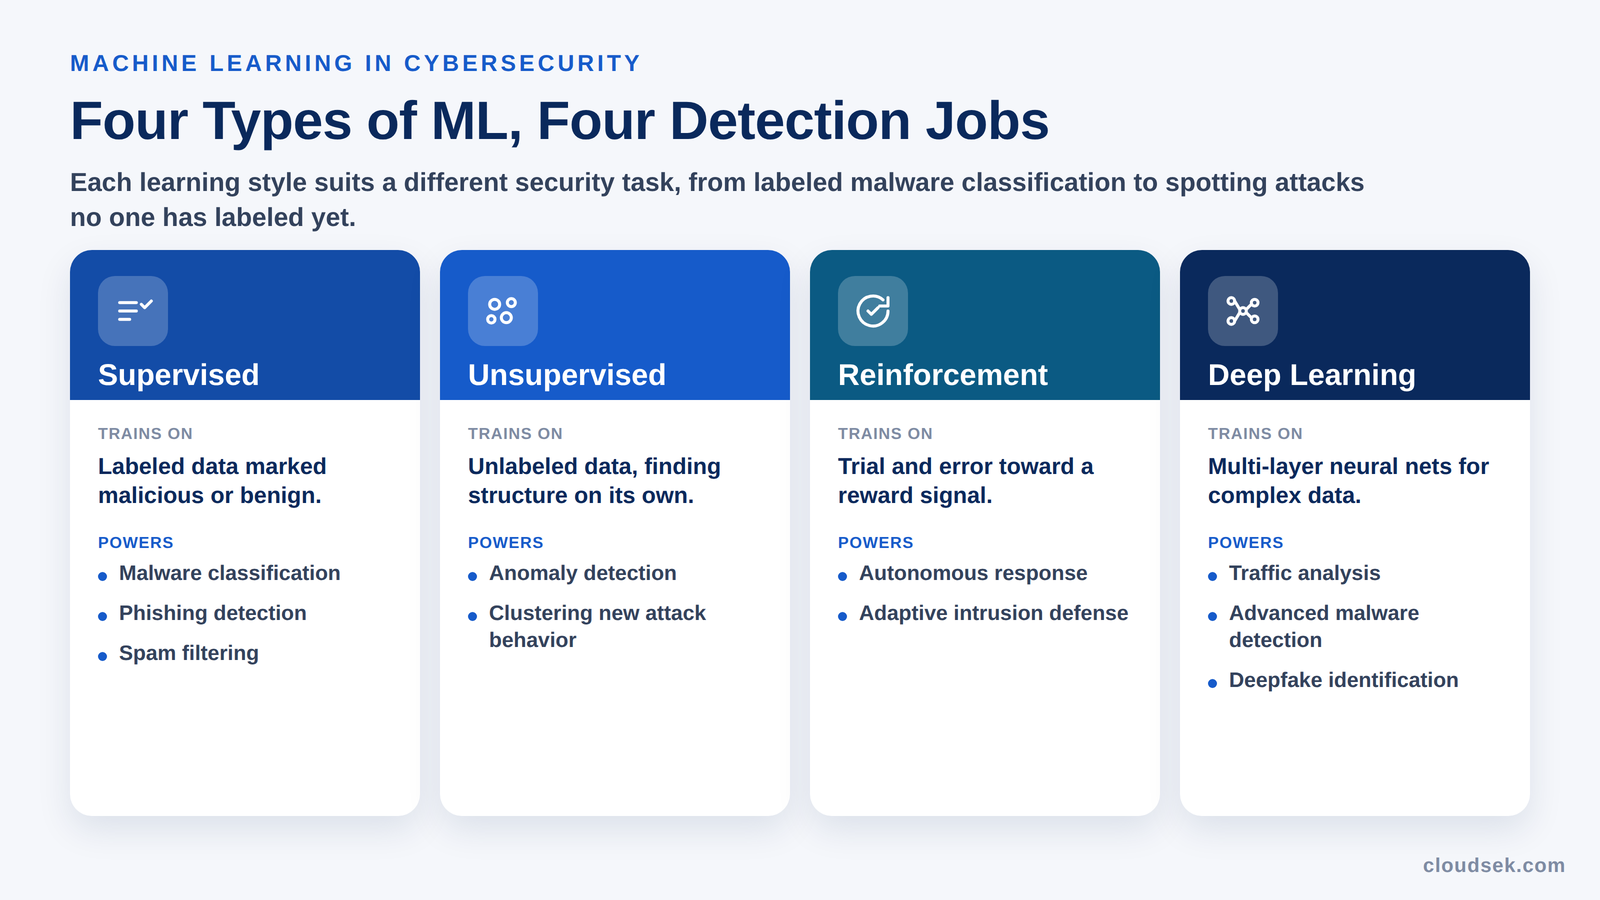
Supervised learning trains models on labeled data, where each sample is marked malicious or benign. In cybersecurity, it powers malware classification, phishing detection, and spam filtering, because the model learns known-bad patterns and applies them to new samples.
Common algorithms:
Unsupervised learning finds structure in unlabeled data without predefined categories. Security teams apply it to anomaly detection and clustering of new attack behavior, because the model surfaces deviations from normal activity that no one labeled in advance.
Common algorithms:
Reinforcement learning trains models through trial and error toward a reward signal. In cybersecurity, it supports autonomous response and adaptive intrusion defense, where an agent learns which actions contain a threat over repeated attempts.
Common algorithms:
Deep learning uses multi-layer neural networks to model complex, high-dimensional data. It handles traffic analysis, advanced malware detection, and deepfake identification, tasks where patterns run too subtle for simpler models to capture.
Common algorithms:
Machine learning supports detection and response across seven core security functions.
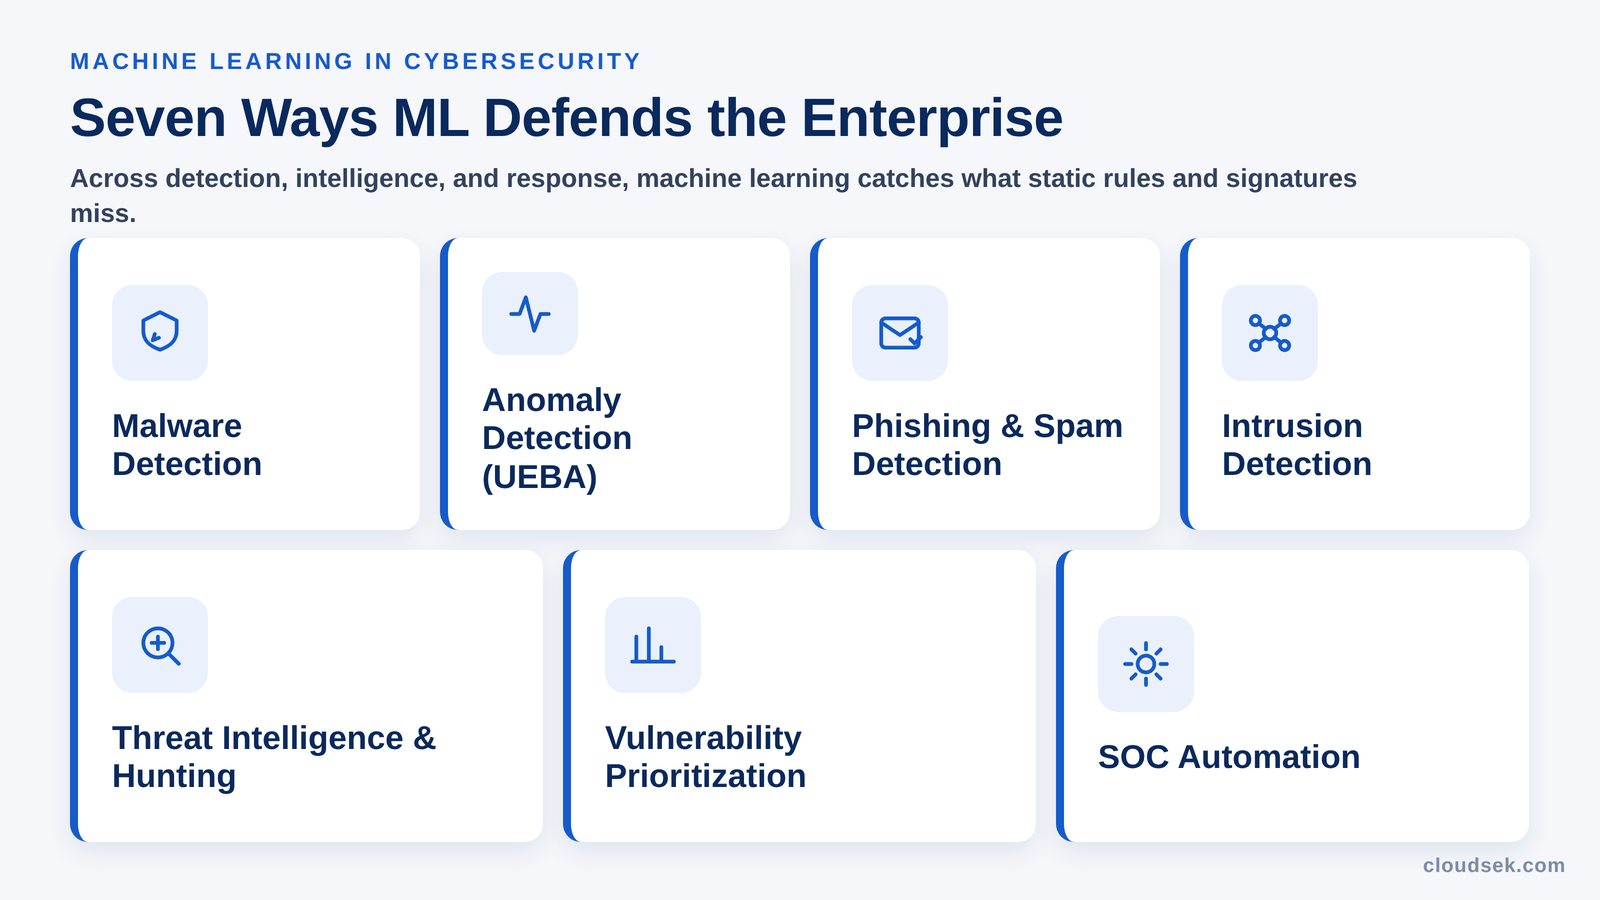
Machine learning classifies files as malicious or benign by learning features from millions of known malware families. Models flag new and modified samples that signature databases miss, including polymorphic variants that change their code to evade detection.
Machine learning establishes baselines of normal behavior for users, devices, and applications. It identifies deviations, such as unusual login locations, unexpected access to sensitive files, or abnormal data transfers, that may indicate compromised accounts or insider threats.
Machine learning scores emails and URLs by language, sender reputation, and structure to filter phishing and spam. Models adapt to new lures faster than static blocklists, reducing successful social engineering.
Machine learning analyzes network traffic, connection patterns, and system activity to identify potential intrusions. By learning to distinguish normal traffic from suspicious behavior, it helps security teams detect emerging threats and reduce false-positive alerts.
Machine learning correlates signals across threat feeds, dark web sources, and telemetry to surface emerging campaigns. It ranks indicators by relevance, letting analysts hunt the threats most likely to target their sector.
Models predict which vulnerabilities attackers are likely to exploit, using exploit activity, asset exposure, and threat context. This prioritization focuses on patching flaws that carry real risk rather than raw severity scores.
Machine learning triages alerts, groups related events, and triggers automated containment for high-confidence detections. Security operations centers apply it to cut alert fatigue and shorten response times.
Machine learning delivers six advantages that manual defense cannot scale to.
Machine learning in cybersecurity mainly carries six limitations that shape how teams deploy it.
Attackers use machine learning to scale and sharpen their operations, turning the technology defenders rely on into an offensive tool. IBM found that 1 in 6 breaches in 2025 involved attackers using AI, most often for phishing and deepfake impersonation.
Offensive machine learning takes three main forms.
Machine learning is a subset of artificial intelligence, not a separate technology. Artificial intelligence is the broad goal of machines performing tasks that need human-like intelligence, while machine learning is the specific method of learning those tasks from data.
In cybersecurity, most tools marketed as AI run on machine learning models trained to detect threats. The distinction matters when evaluating vendors: a claim of AI usually means supervised or unsupervised models under the hood.
CloudSEK applies AI across its security platform to help security teams move from isolated findings to a view of how attackers could chain exposures into an attack path. Rather than positioning machine learning as a standalone detection engine, CloudSEK combines AI-driven correlation, threat intelligence, and continuous external monitoring to identify and prioritize attack paths.
Nexus AI is CloudSEK's attack path intelligence layer. It correlates signals from digital risk, threat intelligence, the external attack surface, AI attack surface, and third-party ecosystems into a unified attack graph. It uses AI agents and agentic reasoning to determine how an attacker could chain exposures such as leaked credentials, vulnerable assets, AI misconfigurations, and vendor weaknesses into an executable attack path.
This approach complements traditional security operations rather than replacing them. While a SOC may investigate individual alerts from endpoint, network, or other internal security tools, Nexus AI focuses on external and AI-related signals to show which combination of exposures could give an attacker a path into the organization and what should be disrupted first.
CloudSEK's AIVigil extends this approach to the AI attack surface. It continuously discovers AI assets—including exposed AI infrastructure, AI endpoints, MCP servers, vector databases, agentic workflows, and shadow AI—and assesses them for AI-specific exposures. These findings can then feed into Nexus AI, where AI-layer risks can be correlated with external threats and third-party exposures to reveal broader attack paths.
CloudSEK's Threat Intelligence provides additional context around threat actors, vulnerabilities, malware, ransomware, and other external threats. Together, these capabilities help security teams understand not only what is exposed, but how an attacker could use those exposures together—shifting the focus from individual alerts and vulnerabilities to the attack paths that matter most.
Machine learning in cybersecurity needs skills in data science, programming, and security fundamentals. Practitioners combine statistics and model building with knowledge of attacks, networks, and threat analysis.
Python is the primary language for ML in cybersecurity, supported by R and Java. Python libraries such as scikit-learn and TensorFlow handle most model building and data work.
No, deep learning is a specialized subset of machine learning. Deep learning uses multi-layer neural networks for large, complex data, while machine learning covers simpler models too.
Machine learning in cybersecurity is moving toward autonomous, agentic systems that investigate and respond with less human input. Adoption keeps expanding as attackers scale their own use of AI.
Yes, small businesses can use machine learning through cloud security tools that build it in. Managed detection services and SaaS platforms deliver ML defense without in-house data scientists.
Yes, modern antivirus and endpoint tools use machine learning to detect unknown malware. ML classifiers identify malicious files by behavior and structure, beyond signature matching.
