🚀 CloudSEK featured in the 2026 Frost Radar™!
Read more


In June 2025, US law enforcement seized BidenCash, a dark web marketplace that had trafficked more than 15 million stolen payment cards and earned over $17 million across three years of operation. Rival shops absorbed its customers within weeks.
BidenCash was one node in carding, the theft, trafficking, and fraudulent use of stolen payment card data. Carding runs as an organized criminal economy, with suppliers, marketplaces, and buyers each playing a defined role, rather than as a scatter of isolated crimes.
Carding is the fraudulent use of stolen credit and debit card data, together with the underground trade that supplies it. A carder is someone who buys, sells, or uses that stolen data to take money or goods.
Monetization is the constant goal. Stolen card details convert into cash through fraudulent purchases, gift-card buying, and resale of goods, which keeps payment cards among the most traded commodities in cybercrime.
Demand shows in the volume. Credit card fraud is the most reported form of identity theft in the United States, according to the Federal Trade Commission's Consumer Sentinel data, which logs hundreds of thousands of complaints every year.
Carding runs as a three-stage pipeline, and different actors often handle each stage.

Card data enters the pipeline through breaches, malware, and skimming. Whoever steals it in bulk rarely uses it directly, selling it instead to buyers on dark web markets who specialize in fraud.
Stolen cards get tested before serious use. Carders run small transactions, often through automated tools, to confirm a card is active and unblocked, since any batch of stolen numbers holds dead entries alongside working ones.
Validated cards convert to value. Carders turn them into resellable goods and cryptocurrency, then route the proceeds through money mules and drop addresses to put distance between themselves and the fraud.
Card data reaches carders through a handful of proven theft methods:

Stolen cards trade in dedicated venues, each serving a different function in the economy.
Pricing tracks the data on offer. A bare card number costs little, while a fullz, a card paired with the holder's full identity such as name, address, and Social Security number, sells for far more because it defeats identity checks.
These markets adapt constantly. CloudSEK's analysis of BidenCash documented the shop expanding beyond cards into SSH server access sold for as little as two dollars, a sign of how carding operators diversify to stay profitable. When one market falls, as BidenCash did in 2025, others absorb the trade.
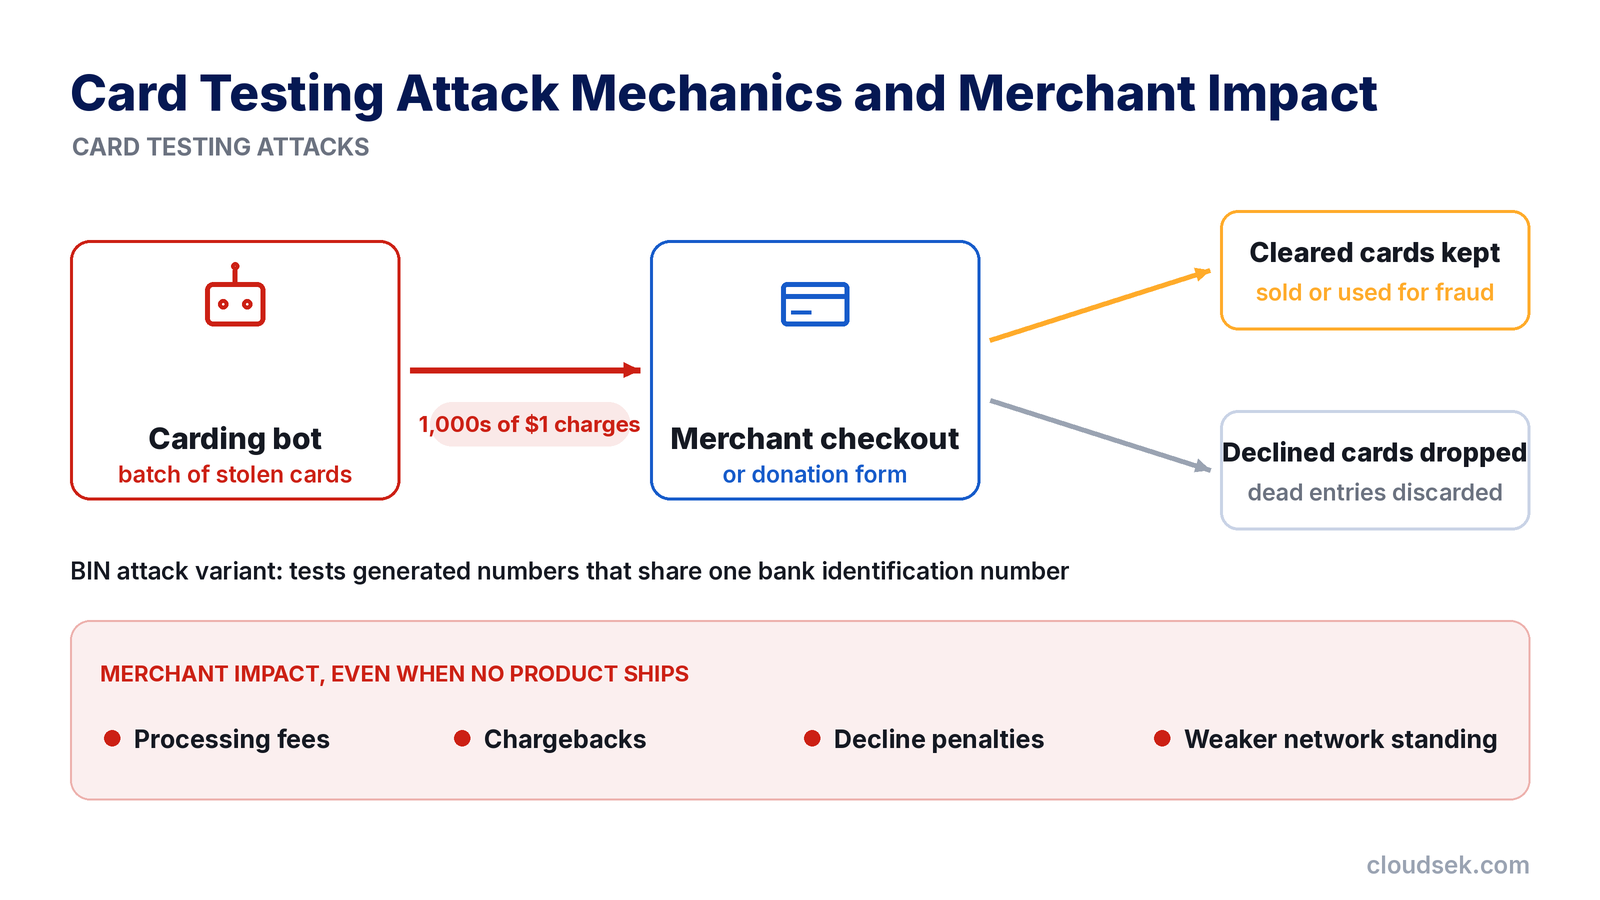
Card testing is where carding collides with legitimate businesses. Before using or reselling stolen cards, fraudsters verify which ones still work, and they do it on real merchants' payment pages.
Automated bots drive the scale. A bot submits thousands of small transactions, often a dollar or less, against a checkout or donation form, keeping the cards that clear and discarding the rest. A BIN attack narrows the effort, generating and testing card numbers that share a single bank identification number.
Merchants absorb the damage even when no product ships. Card testing triggers processing fees, chargebacks, and declined-transaction penalties, and a flood of it degrades a merchant's standing with the card networks.
Beyond card testing, stolen card data feeds several distinct fraud techniques:
Card testing leaves a recognizable footprint that merchants watch for:
Stopping carding takes layered controls on the merchant side and vigilance on the cardholder side.
Most organizations discover carding only when chargebacks arrive, long after their customers' cards reached a dark web shop. Closing that gap means watching the underground markets directly.
CloudSEK's XVigil monitors carding forums, card shops, and Telegram channels for a brand's compromised cards and exposed BIN ranges, surfacing them while there is still time to block and reissue. Threat Intelligence tracks the actors and markets behind the trade, adding context on who is selling and where.
Yes, carding is a serious crime worldwide, prosecuted under fraud, identity theft, and computer-crime laws. Buying, selling, and using stolen card data all carry criminal penalties, including prison.
Skimming is the theft of card data at a physical device or checkout page, while carding is the trafficking and fraudulent use of that stolen data. Skimming supplies the cards; carding monetizes them.
Yes, debit cards are carded alongside credit cards, and often valued higher because they grant direct access to bank funds. Stolen debit data enables both purchases and cash withdrawals.
Merchants with weak payment controls face the highest risk, especially those with low-value checkouts, donation forms, and subscription billing. High transaction volume helps fraudulent tests blend in.
Carders hide behind VPNs, stolen identities, cryptocurrency, and money mules who move goods and funds for them. Layering these steps separates the fraudster from the transaction.
No, EMV chips cut counterfeit card-present fraud but pushed carding toward card-not-present channels. Online payments need only the card number, expiry, and CVV, which carding markets supply.
