🚀 أصبحت CloudSek أول شركة للأمن السيبراني من أصل هندي تتلقى استثمارات منها
اقرأ المزيد


An SSN on the dark web means the number is circulating in criminal breach dumps, marketplaces, or stealer logs, almost always because an organization holding it was breached. Freezing credit at all three bureaus blocks the highest-value fraud channel, and it costs nothing.
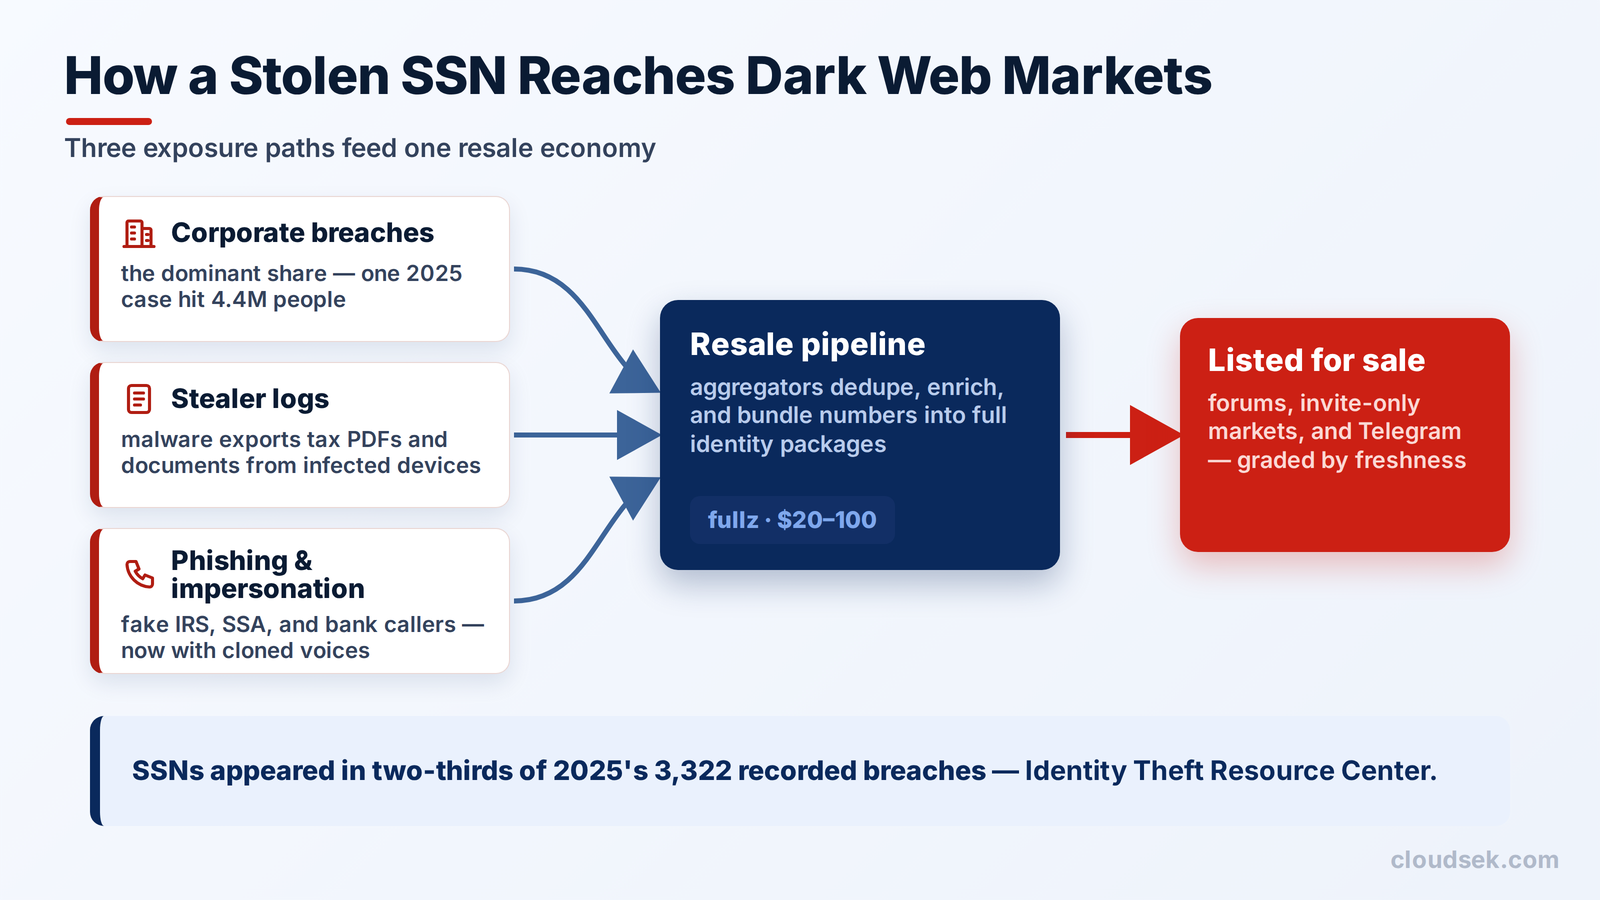
Exposure at this point is the norm rather than the exception. In the Identity Theft Resource Center's 2025 Annual Data Breach Report, Social Security numbers appeared in two-thirds of the year's 3,322 recorded compromises, and SSN-involving breaches nearly doubled between 2021 and 2025.
A dark web alert means a monitoring service matched the number inside a breach database, a criminal forum listing, a stealer log, or a Telegram channel where stolen data trades. It confirms exposure, not fraud. Criminals hold the raw material, and the alert marks the start of a response window before the material gets used.
Severity depends on the bundle, not the number alone. Trustwave SpiderLabs research prices a full identity profile, called fullz in criminal markets, at 20 to 100 US dollars. That package bundles an SSN with name, date of birth, and address, against 5 to 15 dollars for basic contact details.
Single SSN listings trade for a few dollars in bulk. Cheapness reflects oversupply after two decades of breaches, and buyers purchase in volume precisely because pairing each number with fresher identifiers multiplies its fraud value. A lone number in an old recombined dump carries far less immediate risk than a fresh, complete package from a recent breach.
Three exposure paths feed nearly every SSN listing, and a resale pipeline turns each exposure into inventory.
Breaches at organizations holding identity records account for the dominant share of exposed SSNs. In one 2025 example, TransUnion notified more than 4.4 million people that names, Social Security numbers, and dates of birth were compromised through a third-party application serving its consumer support operations.
That case illustrates the structural problem. Even individuals who guard the number carefully depend on every employer, lender, insurer, hospital, and government agency that stores it, plus every vendor those organizations use.
Infostealer malware harvests saved passwords, autofill data, and local documents from infected devices, then exports everything into logs sold on forums and Telegram channels. Tax returns, benefits letters, and onboarding paperwork stored on a personal laptop frequently contain the full SSN.
Stealer logs matter because they bypass the organization entirely. Security teams track leaked credentials across these logs for the same reason criminals prize them: the data arrives fresh, verified, and tied to a living identity.
Fraudsters posing as the IRS, the Social Security Administration, a bank, or an employer collect SSNs directly from the victim. Pretexts follow a pattern: a suspended benefit, a tax discrepancy, or an account lockout that the caller resolves once the victim confirms the number.
Voice cloning raised the ceiling on this path, since a familiar-sounding caller defeats the instinct that flags a stranger. Collected numbers feed the same resale channels as breach data, bundled with whatever else the victim disclosed on the call or form.
Stolen records rarely stay with the original thief. Raw dumps move to aggregators who deduplicate, enrich, and combine sources into fullz packages, which then list on forums, invite-only markets, and Telegram channels graded by freshness and completeness.
CloudSEK's analysis of BreachForums, Leakbase, and XSS documents this economy directly: personally identifiable information ranks among the top traded asset classes, and sellers increasingly package data with access rather than dumping it raw. Takedowns disrupt the market briefly, and activity returns within weeks.
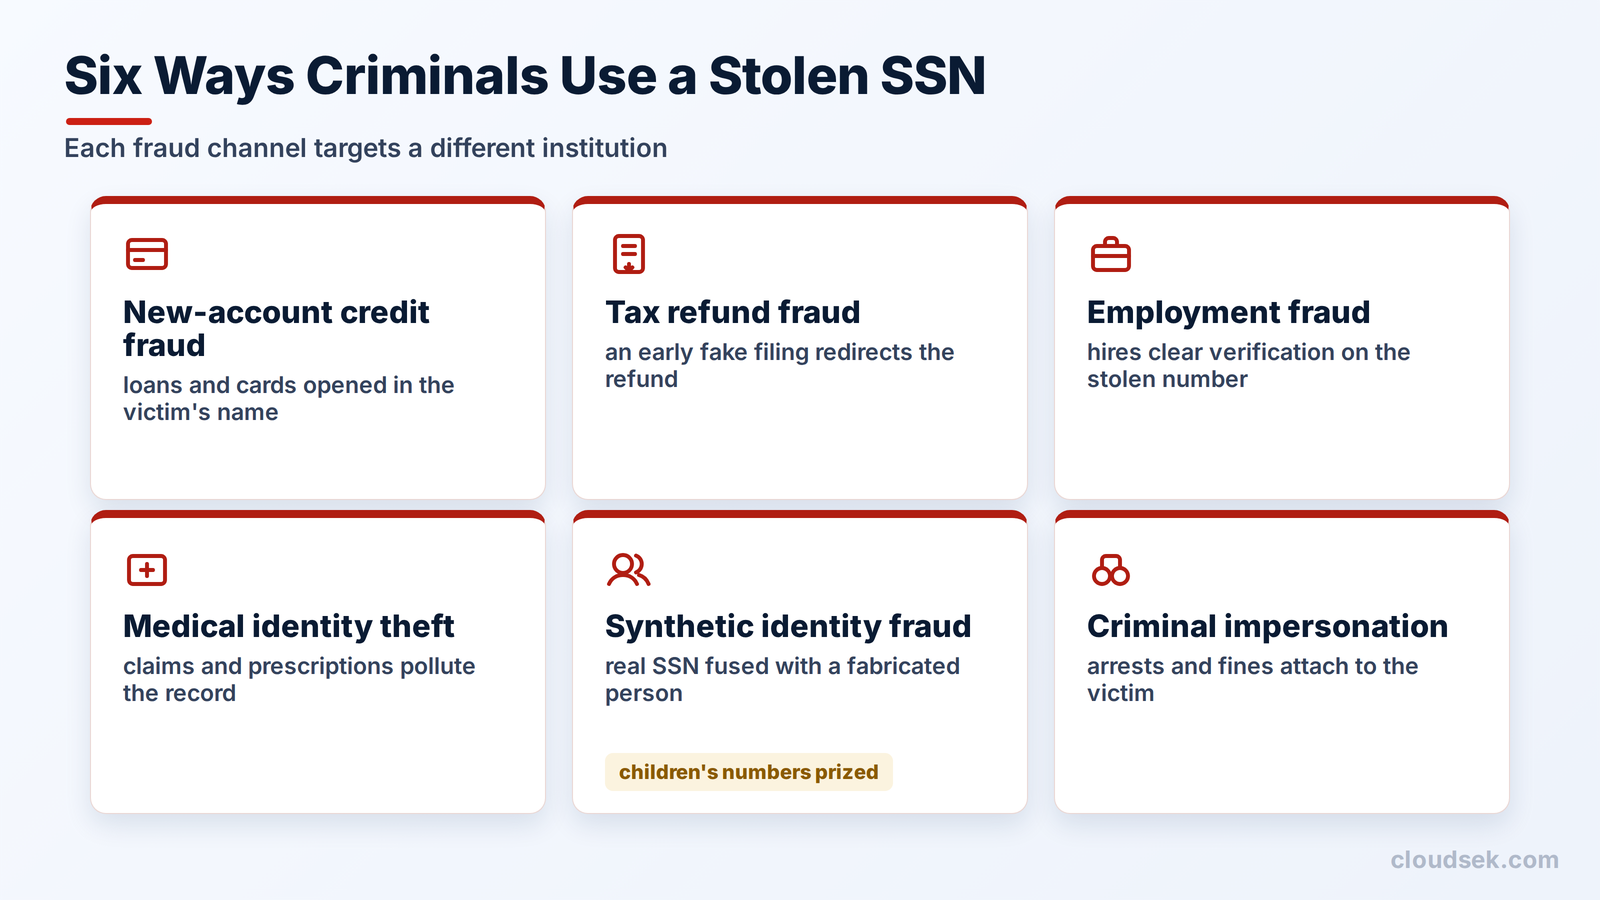
Six fraud categories account for nearly all SSN misuse, and each targets a different institution.
To respond to an SSN found on the dark web, work through 8 steps in priority order. Complete the first three within 48 hours, since they close the highest-value fraud channels.
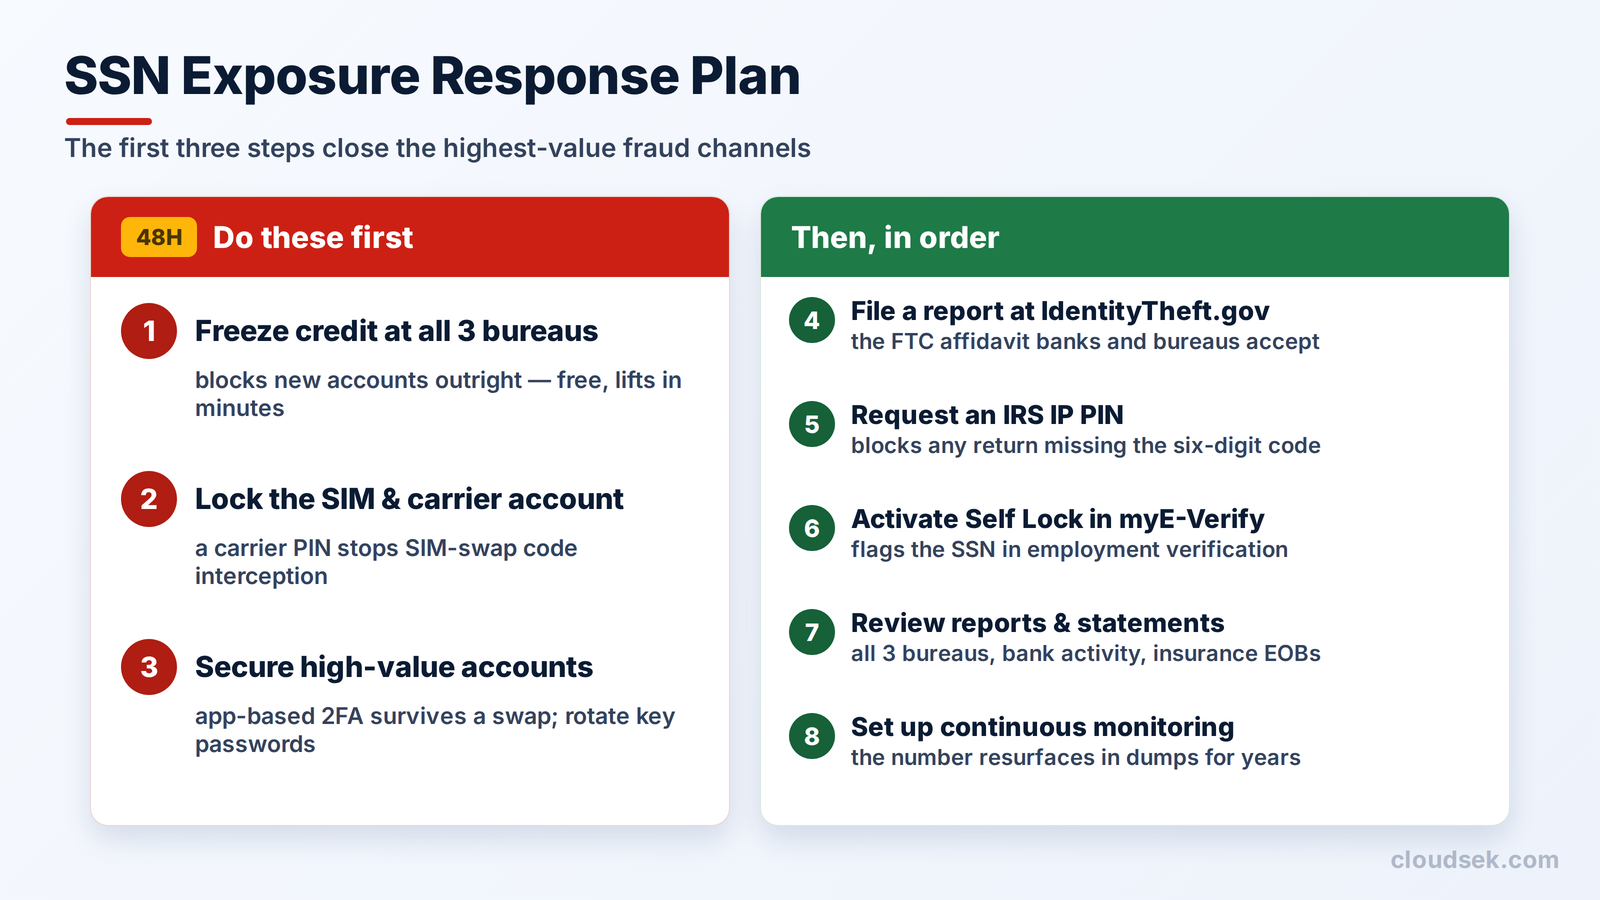
Five free tools each close one fraud channel, and none closes the others. Layering all five covers credit, tax, employment, and benefits misuse at once, which is the coverage a single freeze never provides.
Checking for an SSN on the dark web runs through four channels, ordered from passive to active.
• Continuous monitoring: Dark web monitoring services watch forums, marketplaces, stealer logs, and Telegram channels for specific identifiers and alert on a match. Monitoring is the only forward-looking option, since a scan describes today and the next breach arrives later.
Removal of an SSN from the dark web is not possible. Stolen datasets get copied, resold, and re-uploaded across mirrors and private channels the moment they are listed, so deleting one listing leaves every copy in circulation. No service, paid or otherwise, deletes data criminals already hold.
Replacement is nearly as constrained. The Social Security Administration issues a new number only under narrow criteria, such as ongoing fraud that freezes and alerts failed to stop, and a new number fragments credit history, earnings records, and benefits eligibility.
Containment therefore beats erasure. Every hour spent chasing removal buys nothing, while the freeze, the IP PIN, and Self Lock close the channels through which the exposed number converts into money.
Honest framing comes first: the dominant exposure path is a breach at an organization the individual never chose to trust, so prevention reduces odds rather than eliminating them. Five habits shrink the controllable surface.
Criminals target Social Security numbers because static identifiers outlast every reset. A stolen password expires at the next rotation, and a card number dies with reissuance, while a leaked SSN stays exploitable for decades. Breach activity keeps concentrating on identity records and on the vendors and third parties that process them for exactly that reason.
Organizations sit on the other side of every statistic in this article. A company holding customer or employee SSNs learns about exposure the same way individuals do, through the dark web, and the operational question is whether that discovery happens in hours or after the fraud.
CloudSEK XVigil gives security teams that early discovery, monitoring breach dumps, underground forums, stealer logs, and encrypted channels for organization-specific exposure such as leaked customer PII and employee credentials. Detection at the point of sale on the dark web, rather than at the point of fraud, is what turns a leak into a contained incident instead of a notification letter.
Can a child's SSN be on the dark web?
Yes, a child's SSN can be on the dark web. School, pediatric, and benefits breaches expose children's numbers, and criminals prize them because the credit files stay unmonitored for years.
Does a credit freeze affect your credit score?
No, a credit freeze does not affect a credit score. A freeze blocks new-account checks only, while existing accounts, score calculation, and report access for the individual continue unchanged.
Does the government notify you if your SSN is found on the dark web?
No, the government does not notify individuals when an SSN is found on the dark web. Notification comes from breached companies or from monitoring services.
How do you respond if someone files a tax return using your SSN?
To respond to a tax return filed using a stolen SSN, submit IRS Form 14039, the Identity Theft Affidavit, then file the legitimate return on paper and request an IP PIN.
Is paying an SSN removal service worth it?
No, paying an SSN removal service is not worth it. Circulating copies stay beyond any service's reach, and the free federal tools deliver the actual protection.
Does a dark web alert mean identity theft has already happened?
No, a dark web alert means the SSN appeared in a monitored criminal source. Fraud requires a criminal to act on it, and the alert opens the window to block that use.
