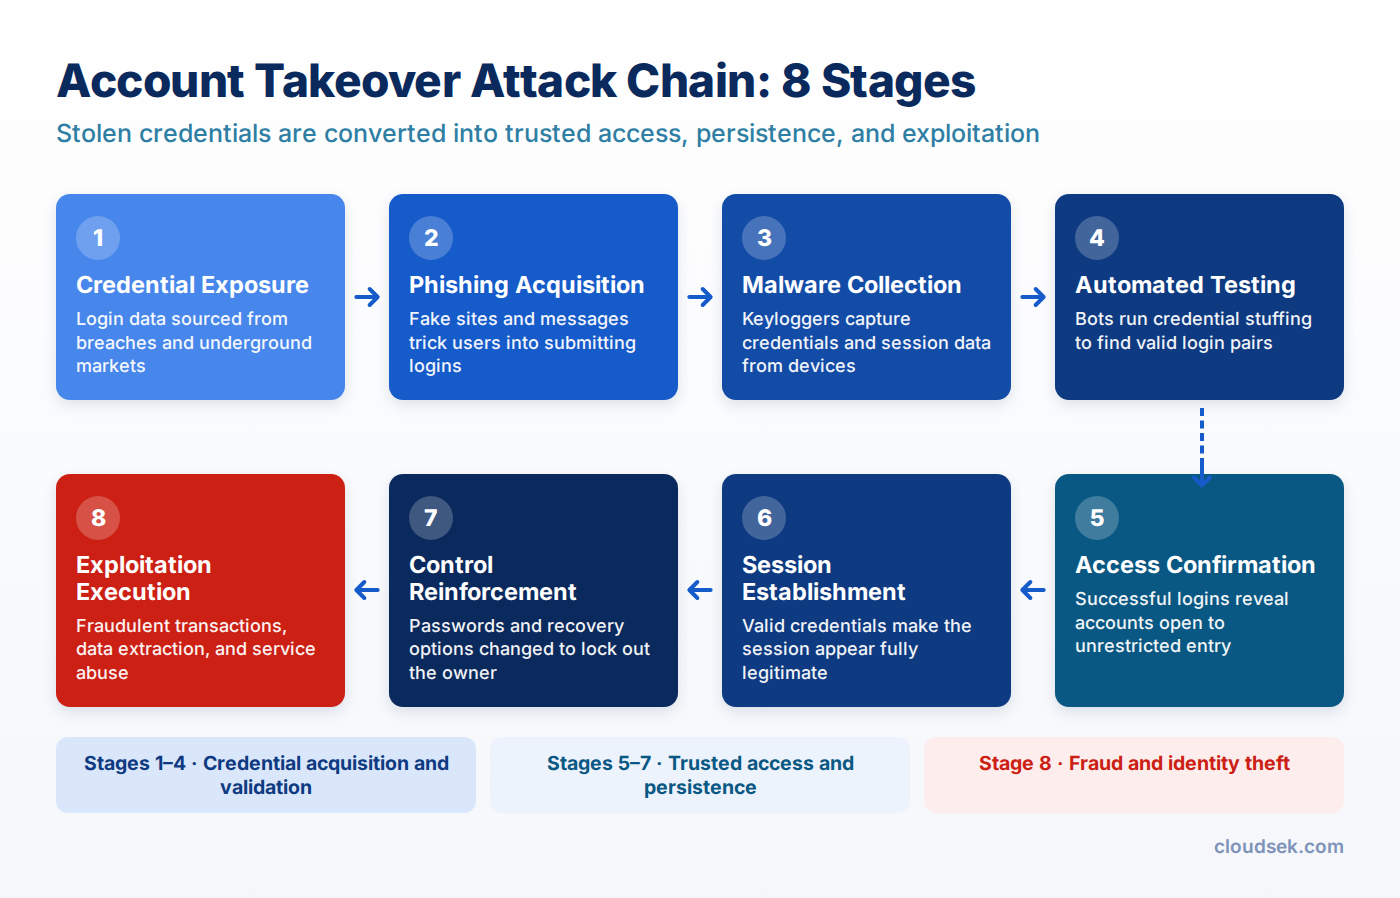
An account takeover attack happens when an unauthorized actor gains and keeps access to a user account using valid authentication credentials that do not belong to them. Attackers source those credentials from breach databases, phishing, malware, or credential stuffing, then use the account for fraud, data theft, or further attacks on connected systems.
Authentication systems validate credentials, not the person supplying them. A stolen password or session token therefore produces a login that looks identical to a legitimate one. That single fact makes account takeover both scalable and difficult to catch.
How Do Account Takeover Attacks Work?
Account takeover (ATO) runs as a connected sequence. Stolen credentials get converted into trusted access, then exploited. Each stage offers a separate intervention point, and catching exposed credentials before they are tested costs far less than detecting fraud afterwards.
Credential Exposure. Attackers obtain login data from breach databases, reused passwords, or underground sources, which often contain large volumes of email-password combinations linked to multiple platforms.
Phishing Acquisition. Phishing campaigns trick users into submitting credentials through fake websites, emails, or messages that appear legitimate.
Malware Collection. Malicious tools such as keyloggers capture typed credentials, stored passwords, and session data directly from infected devices.
Automated Testing. Bots run large-scale login attempts using stolen data, where techniques like credential stuffing help identify valid credential pairs efficiently.
Access Confirmation. Successful login attempts reveal which accounts can be accessed without triggering restrictions, especially on systems with weak authentication controls.
Session Establishment. Attackers enter accounts using valid credentials, and the system treats the session as legitimate since authentication requirements have been satisfied.
Control Reinforcement. Account settings such as passwords, recovery options, and security configurations may be modified to maintain access and prevent the original user from regaining control.
Exploitation Execution. Compromised accounts are used for unauthorized transactions, data extraction, or service abuse, often resulting in financial fraud and identity theft.
What Are the Types of Account Takeover Attacks?
No single technique defines account takeover. Attackers exploit credential trust, session trust, third-party integrations, and recovery workflows in different ways. Each route calls for a different control.
Credential-Based Attacks
Credential stuffing: reusing leaked username and password pairs harvested from unrelated breaches, betting on password reuse.
Brute force: systematically guessing passwords against one account. A brute force attack is noisy, which makes rate limiting effective against it.
Password spraying: testing a small set of common passwords across many accounts, which stays under per-account lockout thresholds.
Social Engineering Attacks
Phishing: persuading users to submit credentials through fake websites, emails, or messages. Targeted spear phishing builds the message from real correspondence.
Malware collection: keyloggers and infostealers capture typed credentials, stored passwords, and session data from an infected device. Much of this malware runs for seconds, then deletes itself.
Session-Based Attacks
Session hijacking: capturing and reusing active session cookies or tokens to bypass authentication entirely, because a persistent session requires no repeated login verification.
Adversary-in-the-middle: relaying a live login through attacker infrastructure to capture the session issued at the end of it. An AitM attack defeats most MFA methods without ever breaking the password.
Identity and Recovery Attacks
SIM swapping: transferring a victim's phone number to an attacker-controlled SIM to intercept SMS-based one-time passwords.
Password reset abuse: manipulating account recovery flows through weak identity verification or predictable security questions. Recovery is the softest route in at many organizations.
Application and Integration Attacks
OAuth abuse: exploiting misconfigured third-party permission scopes to reach an account indirectly, with no credential required and no password change able to revoke it.
API exploitation: targeting backend endpoints that bypass the standard login interface, commonly through improper validation or missing rate limits.
Insider and Third-Party Risk
Insider misuse: authorized users abusing existing internal access, enabled by weak access governance and limited monitoring.
Third-party exposure: credentials leaked through an external breach re-enter attacker ecosystems and get reused elsewhere. One third-party breach therefore spreads across every platform sharing that identity.
Account Takeover vs Credential Stuffing, Brute Force, and Phishing
The distinction matters more than it first appears. Account takeover is the outcome, meaning an attacker is in control of an account. Credential stuffing, brute force, and phishing are three of the methods used to reach that outcome, and a defense aimed at one of them leaves the others open.
Attack
What the Attacker Uses
Goal
Primary Control
Account Takeover
Valid credentials or a live session
Control and keep the account
Session monitoring and least privilege
Credential Stuffing
Leaked username and password pairs
Find which stolen pairs still work
MFA and breached-credential screening
Brute Force
Systematic password guessing
Discover a valid credential
Rate limiting and account lockout
Phishing
Deception aimed at the user
Steal authentication data directly
Email filtering and phishing-resistant MFA
Why MFA Does Not Stop Every Account Takeover
Most published guidance treats multi-factor authentication as the answer to account takeover. It removes the easiest route in, and two categories of attack walk straight past it.
CloudSEK's TRIAD team gained administrator access to BigBear 2.0, a Microsoft 365 phishing-as-a-service operation, and published what the panel held. It contained 5,137 credential records tied to 461 organizations across more than 40 countries, including 4,148 captured session cookies and 474 records showing completed logins where attackers captured the authenticated session created after MFA.
Those 474 sessions show account takeover in its purest form. The password was correct. The MFA challenge was approved. The attacker still ended up holding the session. The operation ran residential proxies matched to each victim's country, which weakened the location checks inside Conditional Access policies. It injected code designed to suppress FIDO2 prompts and steer users toward weaker methods.
OAuth abuse opens the second gap. A granted application scope survives a password change and an MFA re-enrollment, because neither action revokes the consent. Reviewing connected applications belongs in every account takeover response, and teams skip it more than any other.
Account Takeover Attack Examples
These five scenarios cover the routes that dominate incident reports.
Credential stuffing against an e-commerce account: an attacker runs leaked email and password pairs against a retailer's login page. A small percentage succeed because customers reused passwords from an unrelated breach, exposing stored payment methods and order history.
Phishing-based email takeover: a user enters credentials on a convincing fake login page. The attacker signs in, changes the recovery phone number, and uses the mailbox to reset passwords on linked services.
Session cookie theft: malware exfiltrates an active session cookie from a user's device. The attacker imports that cookie into their own browser and reaches the account without ever needing the password.
SIM swap and recovery abuse: an attacker persuades a mobile carrier to port a victim's number to a new SIM. SMS one-time passwords then reset banking and email accounts tied to that number.
Corporate SaaS takeover: an employee's credentials surface in a third-party breach. The same password was reused on a company SaaS account, which opens internal dashboards, documents, and connected integrations.
What Happens After an Account Takeover Succeeds?
Consequences follow a progression: access, then persistence, then data theft, then fraud, then lateral movement into whatever the account can reach.
Identity misuse: impersonation enables fraudulent transactions and communication under the victim's name, which is the mechanism behind most business email compromise.
Financial loss: access to stored payment methods or banking systems creates immediate monetary damage that escalates into large-scale fraud.
Data breach exposure: one compromised account with broad internal access exposes connected systems such as project trackers and knowledge bases, well beyond the account itself.
Lateral movement: a trusted identity opens a route toward higher-privilege accounts, which extends the attack path far past the original login.
Operational disruption: investigation, containment, and recovery consume internal resources and delay regular work for weeks.
Compliance exposure: failing to secure user accounts triggers data protection violations, audits, and financial penalties.
Long-term recurrence: leaked credentials keep circulating across attacker ecosystems, which raises the odds of repeated compromise even after recovery.
How Are Account Takeover Attacks Detected?
No single signal proves a takeover. Detection works by correlating several of these across one identity and a short window.
Location and device anomalies: logins from unusual locations, unrecognized devices, or impossible travel between distant places in an implausibly short time.
Failure-to-success sequences: repeated failed attempts followed immediately by a success, which suggests one guess or one stuffed pair worked.
Unrequested security changes: password, recovery email, or recovery phone changes the user did not initiate, and new MFA device registrations.
Session irregularities: unusual session duration, concurrent sessions from distant locations, or a session that continues after the user signs out.
Abnormal account activity: unexpected transactions, bulk data downloads or exports, new mailbox forwarding rules, and unusual API calls.
New OAuth consents: third-party applications granted access during the suspected window, which persist after other remediation.
Applied continuously instead of checked after the fact, these categories become a working detection set. A security operations workflow that joins them across identity, endpoint, and application logs catches takeovers that no individual alert would surface.
How Can Organizations Prevent Account Takeover Attacks?
Prevention works in layers, because no single control covers every route described above.
Deploy MFA and passkeys: add verification beyond the password, and prefer phishing-resistant methods such as FIDO2 on high-value accounts, since those resist the relay attacks described earlier.
Screen against breached credentials: reject known-exposed passwords at signup and reset, and enforce uniqueness to limit damage from external leaks.
Monitor exposed credentials externally: track breach databases and dark web sources for organization-specific leaks before attackers test them.
Rate-limit and detect bots: restrict login attempts within a defined window, and use challenges selectively when risk indicators appear, never on every login.
Secure session tokens: keep session lifetimes short, handle cookies securely, and require re-authentication for sensitive actions such as payment or recovery changes.
Harden password reset workflows: strengthen identity verification in recovery, so the reset flow does not become an easier route in than the login page.
Audit APIs and OAuth scopes: validate API requests, enforce token management, and review third-party consents on a fixed schedule, not at incident time.
Apply least privilege: limit what any single account can access. Zero trust conditions cap the blast radius when one is taken over.
How to Respond to an Account Takeover
Order matters here, because the most common remediation error is resetting a password while the attacker's session stays live.
Revoke every active session first. Invalidate session tokens and refresh tokens before anything else. A password reset alone leaves a stolen session working.
Reset credentials and re-enroll MFA. Remove any authentication method or recovery detail added during the exposure window, since attackers register their own early in the intrusion.
Review connected applications and OAuth grants. Revoke consents granted during the window. These survive password and MFA changes, and they are the most commonly missed persistence mechanism.
Audit account configuration. Check forwarding rules, delegate permissions, filters, and API keys created or modified while the attacker held access.
Investigate the compromise window. Reconstruct login activity, identify what was accessed or exfiltrated, and establish how the credential was obtained.
Check for lateral movement. Search connected systems for the same source addresses and for other accounts showing the same pattern.
Notify and monitor. Inform affected users and any parties whose data was reachable, then watch the account closely for renewed attempts.
Which Industries Are Most Affected by Account Takeover Attacks?
Industries with high-value user accounts, stored financial data, and frequent authentication activity face greater exposure to account takeover risks. Credential compromise is not limited to consumer-facing platforms. In Australia's FY2024–25 cyber threat reporting, compromised accounts or credentials represented 19% of reported cyber incident types affecting critical infrastructure.
Banking and financial services: direct access to funds and transaction systems, which makes fraud immediate and hard to reverse.
E-commerce: stored payment details, saved addresses, and order histories that support both direct fraud and identity theft.
SaaS and technology: one set of business credentials reaches data, integrations, and privileged administrative functions across a whole tenant.
Social media: identity, impersonation, and a ready-made distribution channel for scams aimed at the victim's contacts.
Gaming: digital assets, in-game currency, and stored payment methods, with resale markets that make monetization quick.
Healthcare: sensitive patient records, and the costliest breaches of any sector at $7.42 million on average according to IBM's Cost of a Data Breach 2025. Connected IoMT environments widen the reach of a single compromised clinical account.
Why Account Takeover Remains a Threat in 2026
Every input feeding account takeover continues to scale year on year. Credential stuffing, infostealer logs, session cookie theft, phishing, and password reuse all benefit from automation. AI-assisted lures are harder to spot than the templated ones that preceded them.
Wider adoption of passkeys and MFA is closing the easiest paths. That progress has shifted attacker effort toward session hijacking and OAuth abuse, which need no password at all. Defending against account takeover in 2026 means defending the session and the consent, not only the login.
Account Takeover FAQs
Is account takeover the same as identity theft?
No. Identity theft misuses a person's identity broadly across new accounts and credit. Account takeover is control of one existing account.
Is account takeover illegal?
Yes. Accessing an account without authorization is a criminal offence under computer misuse laws in most jurisdictions, whatever the attacker does next.
Is an account takeover a reportable data breach?
It varies by jurisdiction and by what the account reached. Under GDPR, unauthorized access to personal data triggers the 72-hour notification assessment.
Who is liable when a customer account is taken over?
It depends on the sector and the contract. Financial regulations shift much of the loss to the provider, while most consumer platform terms do not.
How long does an account takeover go unnoticed?
It varies with monitoring quality. Takeovers that avoid visible changes and mimic normal usage can run for weeks before anyone notices.
Can an account with a strong, unique password still be taken over?
Yes. Session theft, SIM swapping, and OAuth abuse all bypass the password entirely, so password quality is irrelevant to those routes.
How is account takeover different from a data breach?
A breach exposes data from a system. Account takeover is unauthorized use of one identity, and it commonly follows a breach elsewhere.
Catching Account Takeover Before the Login
Account takeover has no single moment of compromise. The credential leaks in one place, the login happens in another, and persistence gets established somewhere else again. Treating each stage as an isolated alert misses the pattern connecting them.
The chain starts before any login attempt. CloudSEK XVigil tracks where an organization's credentials, session cookies, and API keys surface across dark web forums, paste sites, and messaging channels. That catches exposure at the point it becomes usable, not after it has been tested against a live account. Guidance on preventing account hijacking covers the user-side controls that sit alongside it.
Pastebin is a free site for sharing plain text and code via a link. How Pastebin works, its legitimate uses, security risks, and how attackers abuse it.
Personally identifiable information (PII) is any data that identifies a specific person. PII types, examples, exposure risks, and the laws that govern it.